Cloud Detection and Response
Cloud Detection & Response That Stops Threats Fast
AgileBlue's Autonomous SecOps platform continuously monitors cloud environments to detect threats, investigate suspicious activity, and contain compromised identities. With autonomous response capabilities and 24/7 SOC expertise, AgileBlue helps protect AWS, Azure, Google Cloud, and hybrid environments without adding complexity to your security operations.

Benefits + Features

Continuous Cloud Detection & Response
We continuously monitor activity across your environment, surfacing real threats fast. No lag, no noise, just clarity.

Identity Risk Detection
Flags compromised or misused accounts in real time, so your team can move fast to disable access, revoke sessions, and strip privileged roles before damage spreads.

Credential Hardening
Surfaces stolen or exposed keys and secrets immediately, with clear guidance to rotate, revoke, and re-authorize under least-privilege principles.

Complete Cloud Visibility
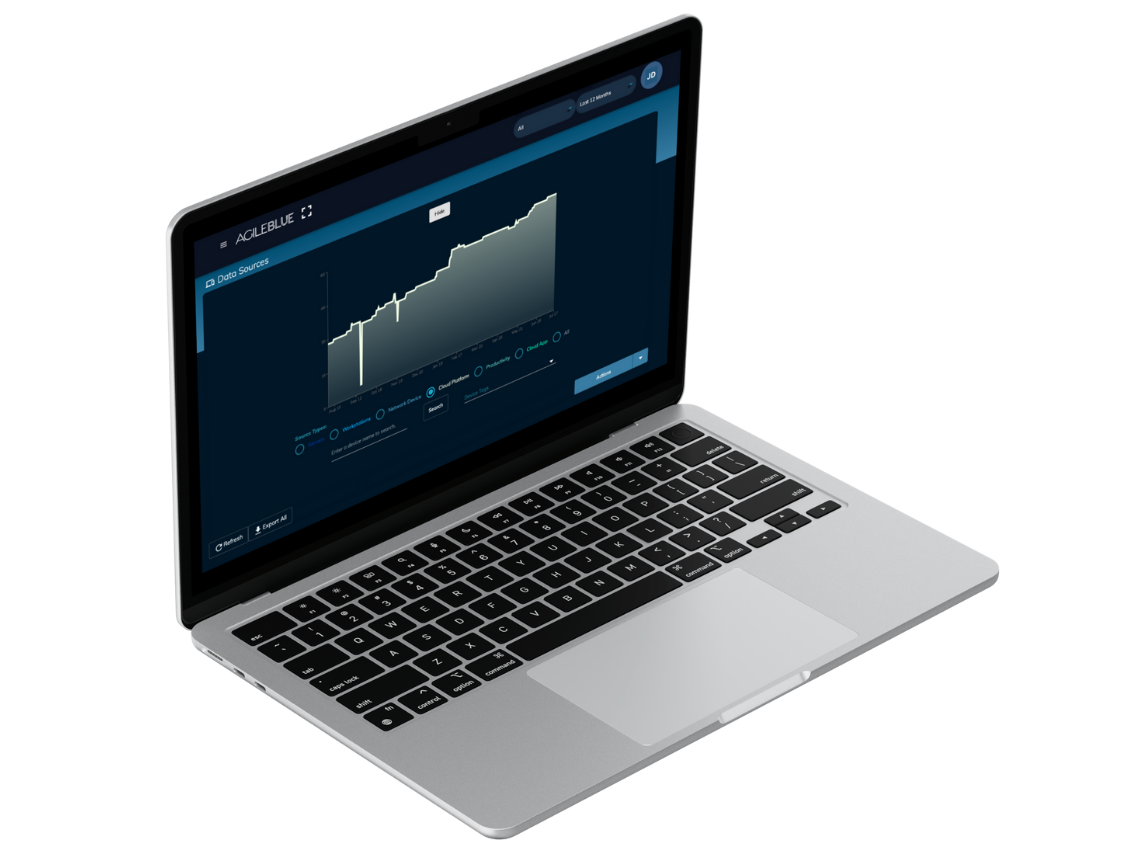
Monitor activity across multi-cloud environments with complete transparency, from identity to workload to data flow.
Cloud-Native Defense That Moves as Fast as You Do
AgileBlue delivers real-time cloud detection and visibility across your environment. From securing workloads and containers to monitoring identities and misconfigurations, our Autonomous SecOps platform adapts to your cloud, not the other way around. Streamlined, scalable, and backed by 24/7 support, it’s the protection modern environments demand.
-
Continous monitoring across AWS, Azure, GCP
-
Simple setup with now agents or performance drag
Autonomous Cloud Response: From Detection to Containment
Detecting a compromised cloud identity is only the beginning. AgileBlue's Autonomous Cloud Response extends protection beyond alerts by automatically containing affected identities when malicious activity is confirmed. With customer-controlled automation, documented response actions, and 24/7 SOC support, organizations can reduce the time between identifying a threat and stopping unauthorized access.

Cloud Detection & Response FAQ
Cloud detection and response (CDR) continuously monitors cloud environments to identify, investigate, and respond to cyber threats. It analyzes cloud activity, detects suspicious behavior, and helps stop attacks before they spread. AgileBlue combines AI-native threat detection, automated investigation, autonomous response, and 24/7 SOC expertise to protect cloud environments and reduce the burden on internal security teams.