Arctic Wolf and AgileBlue’s AI-native SecOps platform both now compete on agentic automation, not just on whether AI is present. Since Arctic Wolf launched its Aurora Agentic SOC in March 2026, the real distinction between the two approaches is architectural: whether AI was the platform’s starting point or a capability layered onto an established concierge model.
Arctic Wolf built its reputation on a concierge security model, dedicated human analysts monitoring, investigating, and coordinating response on a client’s behalf. With Aurora, Arctic Wolf added an agentic AI layer designed to triage, investigate, conduct threat hunting, and respond, while maintaining its managed SOC and Concierge Experience. AgileBlue took the opposite path: AI as the foundation the platform was built around, with a human SOC team layered on top for oversight and escalation.
Cybersecurity Platforms That Reduce Operational Complexity
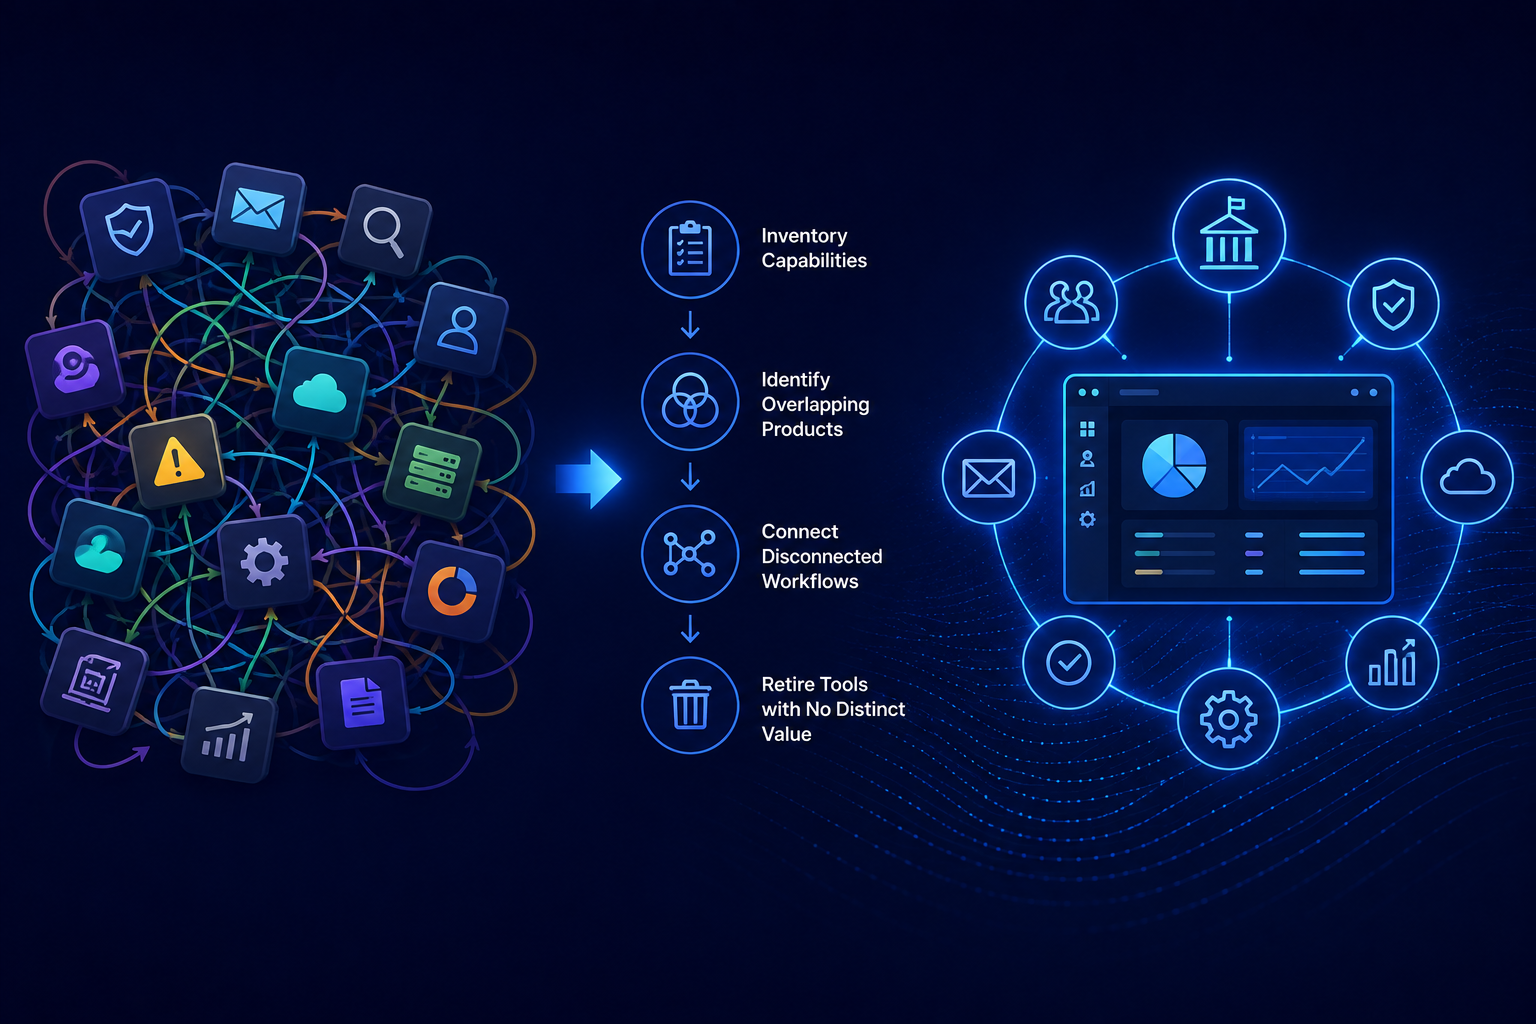
Operational complexity in a SOC typically comes from tool fragmentation, alert overload, and the manual correlation work needed to connect activity across systems. Arctic Wolf’s Aurora is designed to reduce this complexity through AI-driven triage, investigation, and response, with human experts remaining involved when additional judgment or context is needed. AgileBlue takes a unified approach, using autonomous investigation, decisioning, and response to reduce routine analyst workload across the security environment, while its 24/7 U.S.-based SOC provides human expertise and oversight when it matters most.
The practical difference isn’t “manual vs. automated” anymore. It’s where in the workflow the automation sits, and how much of the Tier 1/Tier 2 workload it actually removes versus simply summarizes for a human reviewer.
Can MDR Platforms Replace Multiple Cybersecurity Tools?
Arctic Wolf and AgileBlue both use agentic AI to reduce manual security work while retaining human expertise for oversight, escalation, and higher-impact decisions. The primary difference is not whether either provider uses AI. Buyers should compare how each company delivers security operations, governs autonomous response, works with existing technology, supports the customer, and reports performance.
Arctic Wolf (Aurora Agentic SOC) vs. AgileBlue
| Aspect | Arctic Wolf Aurora Agentic SOC | AgileBlue AI-Native SecOps |
| Operational Model | AI-led security operations delivered through the Aurora Agentic SOC (launched March 2026), with humans in and on the loop. Customers continue working with a named Concierge Security Team. | AI-native, human-supported security operations. Sapphire AI performs detection, investigation, decision-making, and approved response, backed by a 24/7 U.S.-based SOC. |
| Agentic Investigation | Aurora’s Swarm of Experts coordinates hundreds of specialized agents across triage, investigation, response, threat hunting, risk management, and other security activities. | Sapphire AI correlates activity across the environment, investigates suspicious behavior, closes cases determined to be benign, and prioritizes incidents requiring additional attention. |
| Response Model | Aurora agents can execute response tasks and resolve defined security cases. The specific containment and remediation actions included, and when customer approval is required, may vary by service. | Sapphire AI initiates response actions according to each customer’s documented preferences. Customers determine which actions may be autonomous, which involve AgileBlue analysts, and which remain with the internal team. |
| Technology Strategy | Supports integrations with existing security technologies while also offering native capabilities across endpoint security, detection and response, risk management, cloud monitoring, security awareness, and related areas. | Brings detection, investigation, response, centralized security data, endpoint visibility, cloud security, vulnerability management, threat exposure management, and additional capabilities into one operating environment. It also supports integrations with existing technologies. |
| Human Support | The Concierge Security Team provides named security experts, strategic recommendations, posture reviews, and ongoing guidance. Human experts also oversee agentic outcomes and higher-impact decisions. | AgileBlue’s 24/7 SOC analysts provide continuous oversight and respond when an incident requires additional context or human judgment. Customers also receive dedicated success support and can add Strategic Advisory services. |
| Performance Reporting | Arctic Wolf reports that Aurora has resolved some investigations in as little as 12 seconds and has introduced Mean Time to Trusted Action as an additional measurement. Buyers should confirm which metrics apply to their contracted services. | AgileBlue reports an average MTTD of 4.6 minutes and an MTTR averaging 1.8 minutes with AI turned on. Customers can track MTTD, autonomous MTTR, and analyst MTTR within their dashboard to understand how quickly threats are identified and handled. |
| Potential Fit | May fit organizations that value a named concierge relationship, want to preserve parts of an existing security stack, and prefer a fully managed agentic SOC with ongoing strategic guidance. | May fit mid-market organizations seeking configurable autonomous response, broader platform consolidation, U.S.-based SOC support, and direct visibility into autonomous and analyst-led performance. |
Neither operating model is automatically simpler for every organization. Arctic Wolf may allow a customer to preserve more of its existing technology while placing the management burden with its Agentic SOC and Concierge Security Team. AgileBlue may allow a customer to consolidate more security capabilities while defining how Sapphire AI and SOC analysts respond to incidents.
Prospective customers should validate which tools can be retired, which response actions are included, what work remains with the internal team, and how each provider defines and reports security outcomes.
What Should Lean Teams Compare in an Agentic SOC?
Lean security teams should evaluate an agentic SOC based on how much operational work it removes, what actions it can perform, and how clearly it demonstrates results—not simply whether the provider uses AI. The term “agentic” can describe significantly different levels of automation, customer control, and human involvement.
Important evaluation areas include:
- Autonomous Investigation Scope: Determine which activities AI agents perform independently, including signal correlation, evidence collection, timeline construction, threat validation, and case closure. Ask what percentage of investigations are completed without waiting for a human analyst.
- Response Authority: Confirm which containment and remediation actions the platform can execute autonomously. Teams should understand whether it can isolate endpoints, disable accounts, block malicious activity, or remove attacker persistence—and which actions require analyst or customer approval.
- Customer-Defined Guardrails: Look for the ability to establish response preferences according to the organization’s risk tolerance and operational requirements. The provider should clearly document which actions are pre-approved, which require escalation, and how those rules can be updated.
- Telemetry and Attack Visibility: Review which endpoints, identities, email systems, networks, cloud environments, applications, and security tools contribute data. Effective correlation depends on having sufficient visibility across the environment, not merely automating the analysis of a limited set of alerts.
- Work Reaching the Internal Team: Ask what customers actually receive after the provider’s technology and analysts complete their work. Lean teams should receive validated incidents with clear context and response guidance—not another queue of alerts requiring internal investigation.
- Human Expertise and Escalation: Understand when human analysts become involved, what qualifications they possess, and whether support is continuously available. Human involvement should be clearly defined for complex investigations, novel threats, high-impact response decisions, and customer communication.
- Tool Consolidation and Integration: Identify which existing products can be retained, integrated, replaced, or retired. A platform that supports broad integrations may preserve prior investments, while greater consolidation may reduce licensing costs and management overhead.
- Performance Measurement: Require transparent definitions for Mean Time to Detect, Mean Time to Investigate, Mean Time to Contain, and Mean Time to Respond. Buyers should also ask whether autonomous and analyst-led response times are measured separately and whether the methodology is visible to customers.
- Implementation and Ongoing Management: Compare deployment timelines, integration requirements, tuning responsibilities, customer staffing needs, and ongoing administrative work. A sophisticated agentic SOC provides limited operational benefit if the internal team must continuously build, maintain, and govern its workflows.
The right model is the one that measurably reduces the work remaining with the internal team while preserving appropriate visibility and control. Product demonstrations should therefore show the complete workflow—from the first security signal through investigation, decision, response, human escalation, and final reporting.
Why AgileBlue for Reducing SOC Complexity and Operational Overhead
Our AI-native SecOps platform was designed from the ground up to deliver enterprise-grade security tailored for mid-sized organizations. It integrates nine critical security operations, including Sapphire AI for autonomous detection and response, unifying endpoint, network, and cloud security in a single system.
We automate large portions of Tier 1 and Tier 2 analyst workload while auto-closing benign alerts to drastically reduce false positives. Our platform averages a Mean Time to Detect (MTTD) in 4.6 minutes, enabling faster, more effective responses before cyber threats escalate. Supported by a 24/7 U.S.-based SOC analyst team, we combine AI speed with human expertise and oversight.
This collaborative SOC model acts as an extension of your team, providing transparency and proactive communication instead of simply sending alerts. Our approach has helped us maintain a 96% customer retention rate among mid-market clients, proving our platform and support deliver operational simplicity and strong protection.
Schedule Your Free Demo of Our AI-Native SecOps Platform
If you are evaluating alternatives to Arctic Wolf or want to reduce SOC complexity and operational overhead, explore how our AI-native SecOps can transform your cybersecurity posture. Request a personalized demo to experience the unified platform’s speed, simplicity, and responsiveness. Discover how to consolidate your toolset and streamline SOC workflows while enhancing detection and response effectiveness.
FAQs
Q: Does Arctic Wolf use Agentic AI?
A: Yes. Arctic Wolf launched the Aurora Agentic SOC in March 2026. Its Swarm of Experts uses hundreds of specialized AI agents to support triage, investigation, response, threat hunting, risk management, and other security activities. Human experts remain involved in oversight, escalation, strategic guidance, and higher-impact decisions.
Q: What is the main difference between Arctic Wolf and AgileBlue?
A: Both providers combine agentic AI with human security expertise, but they deliver those capabilities differently. Arctic Wolf provides an AI-led Agentic SOC alongside a named Concierge Security Team. AgileBlue delivers an AI-native SecOps platform in which Sapphire AI and 24/7 U.S.-based SOC analysts respond according to each customer’s documented preferences. Buyers should compare customer control, included response actions, platform capabilities, human support, and performance reporting.
Q: How can a lean team determine which platform will reduce more operational work?
A: Ask each provider to demonstrate the complete workflow from initial signal through investigation, response, escalation, and reporting. Teams should compare how many cases require customer involvement, which remediation tasks remain internal, how many existing tools must still be managed, and what ongoing administration the service requires.
Q: Is human expertise still part of the SOC model?
A: Yes, on both sides. Arctic Wolf’s concierge team leads investigation and response with Aurora’s help; AI-native platforms pair autonomous detection with a 24/7 SOC team for escalation and governance. The difference is where in the workflow that human review happens, not whether it happens.