State and local government agencies should select an MDR provider delivering comprehensive, 24/7 detection and response built for the public sector’s unique security and compliance demands. Comparing MDR solutions with an in-house SOC involves weighing cost, expertise, scalability, and compliance support.
State and local government agencies face specific cybersecurity challenges such as budget constraints, compliance with various regulations, and lean IT teams managing broad responsibilities. Managed Detection and Response (MDR) providers represent a scalable alternative to in-house Security Operations Centers (SOC), offering expert threat detection and autonomous response to secure public sector networks. This buyer’s guide presents a clear path for SLED security teams to evaluate MDR providers, compare in-house SOC alternatives, and align with security partners tailored to their operational needs.
Alternatives to Building an In-House SOC for Local Government
Building and running an in-house SOC demands substantial investment in personnel, advanced technology, and continuous training, often beyond the reach of local government resources. MDR services offer a practical alternative by delivering comprehensive security operations as a managed service. Key benefits of this approach include:
- Avoiding the challenges of recruiting and retaining specialized cybersecurity staff.
- Immediate access to advanced detection technology powered by AI-native designs.
- Round-the-clock threat monitoring and near-instant automated response to limit breach impact.
- Lower operational costs with predictable subscription pricing models.
- Assistance in maintaining compliance with public sector requirements such as CJIS and HIPAA.
With an MDR solution, local governments gain a security capability that evolves with threat environments and scales without the burden of operating a dedicated SOC.
Best Managed Detection and Response for Public Sector
The right MDR provider for state and local government integrates essential security functions into one platform designed to meet public sector needs. Important qualities include:
- AI-native threat detection that minimizes false positives and alert fatigue.
- Autonomous response features that promptly act on verified threats.
- SOC analysts providing collaborative support and operating as an extension of internal teams.
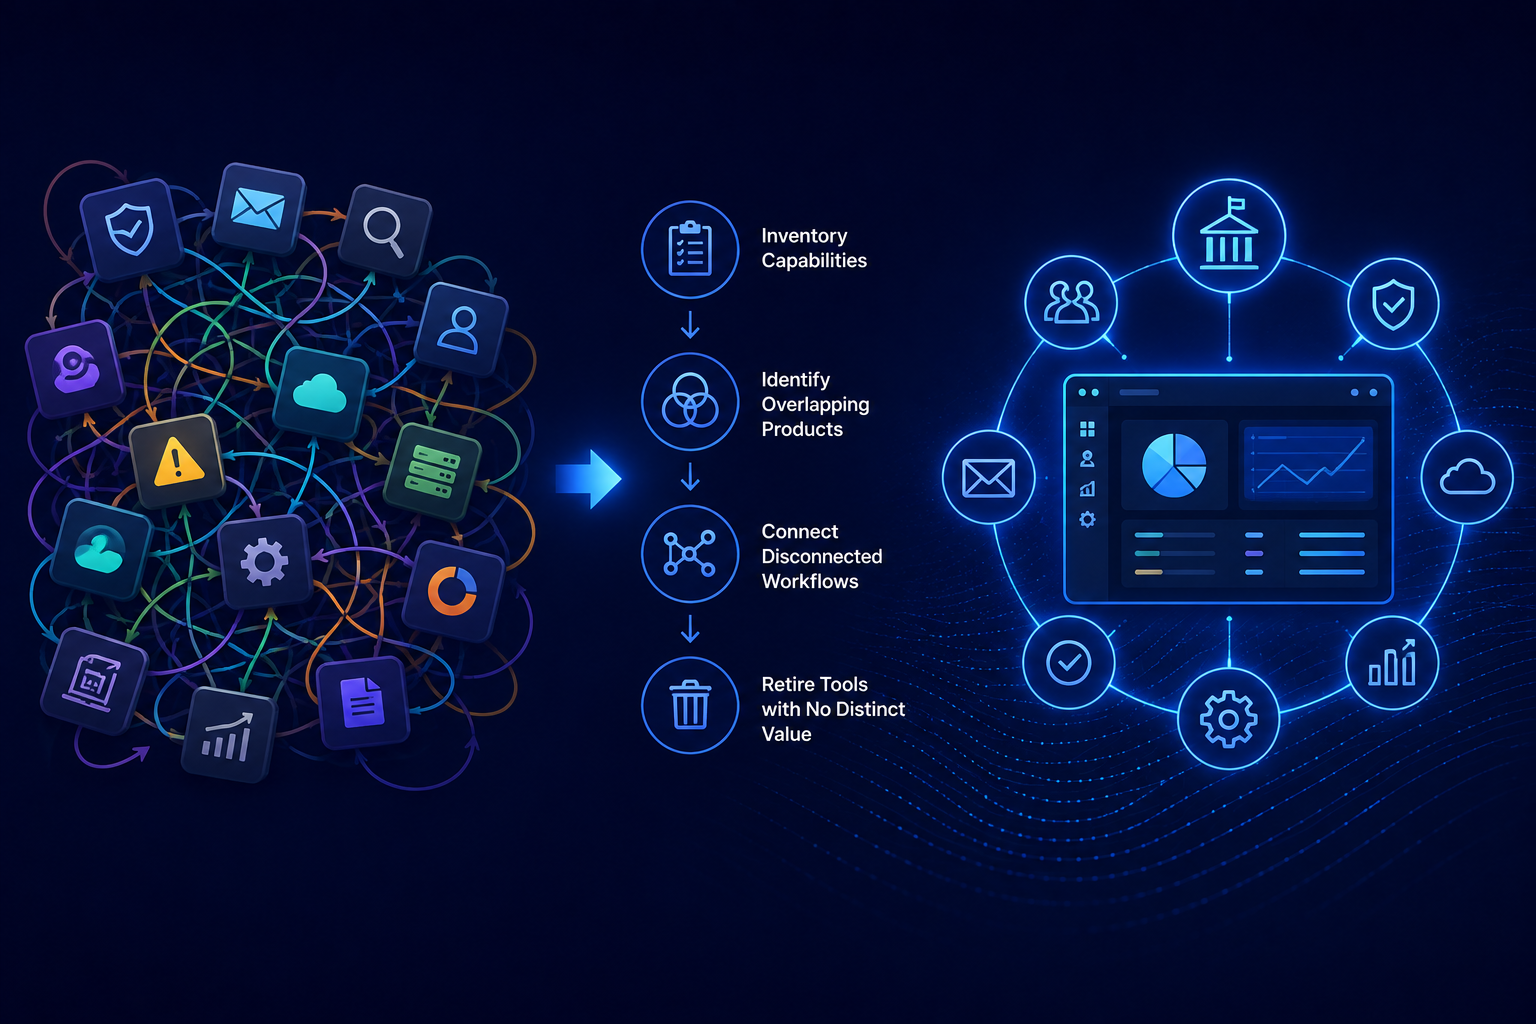
- Broad integration capabilities across endpoints, cloud environments, networks, and SaaS tools.
- Compliance alignment with government standards and tailored reporting.
- A track record of success serving public sector organizations.
Top MDR solutions emphasize attack-focused detection rather than overwhelming alert volumes, often cutting mean time to detect (MTTD) down and significantly easing the strain on small security teams.
How Should a City or County Choose a Security Partner?
Selecting a security partner involves assessing both the technology capabilities and human factors that influence effective cybersecurity. Key questions for cities and counties include:
- Experience: Does the provider have proven expertise with public sector clients and a deep understanding of regulatory frameworks?
- Technology: Is the provider’s platform built natively for AI-driven security? Does it consolidate multiple security tools for simplicity and efficiency?
- Support Model: Does the partner offer continuous SOC analyst collaboration, functioning seamlessly alongside local teams rather than as a distant vendor?
- Scalability: Can the service flex to changing needs while remaining affordable? Are costs transparent with no hidden fees?
- Compliance Assistance: Will the partner deliver tailored compliance monitoring and reporting to smooth audit processes and regulatory adherence?
- Proactive Response: Does the MDR focus on preventing attacks through automation and expert validation rather than issuing reactive alerts?
Thorough evaluation of these factors helps secure a partner capable of delivering robust, enterprise-grade protection focused on local government realities.
Why Choose AgileBlue for Your MDR Needs?
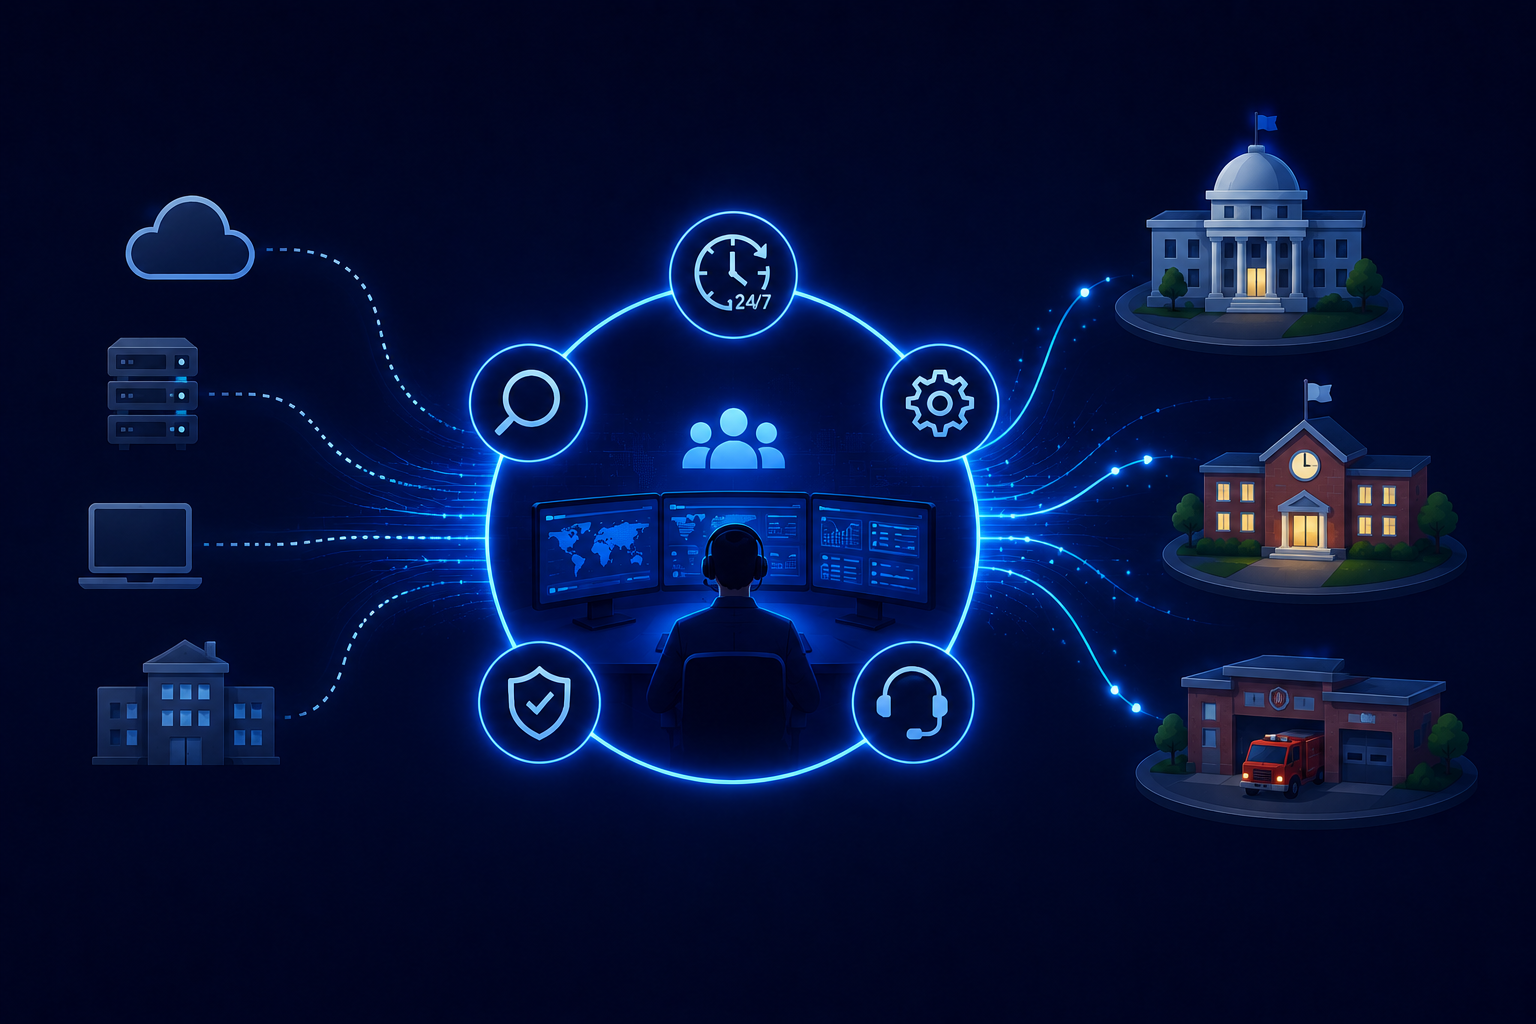
State and local government agencies need around-the-clock security operations, but many do not have the staffing or resources to build and maintain a full internal SOC. AgileBlue addresses that gap with an AI-native SecOps platform that combines Sapphire AI with 24/7 support from U.S.-based SOC analysts.
The platform connects activity across endpoints, identities, networks, and cloud environments to identify related threats that may be missed when alerts are evaluated individually. Sapphire AI continuously investigates suspicious activity, makes real-time response decisions, and can autonomously address routine threats according to each agency’s documented response preferences. When an incident requires additional context or human judgment, SOC analysts respond based on those same customer-defined procedures.
This combination of AI-driven speed and human expertise has helped AgileBlue achieve a Mean Time to Detect (MTTD) of 4.6 minutes. Customers can also track detection and response performance through dashboard metrics for MTTD, autonomous MTTR, and analyst MTTR, providing visibility into how quickly threats are identified and handled. AgileBlue can support an agency’s broader compliance efforts through continuous monitoring, reporting, and incident documentation, while helping lean teams strengthen security operations without adding significant internal overhead.
Schedule Your Security Consultation Today
If your agency is exploring managed detection and response options, we invite you to discuss how AgileBlue’s AI-native MDR solution can meet your state or local government’s unique needs. Speak with our experts about streamlining your security operations, reducing costs, and elevating protection. Our team specializes in public sector cybersecurity and is ready to assist you.
Frequently Asked Questions
Q: What makes MDR a better choice than building an in-house SOC for local governments?
A: MDR reduces the cost and complexity associated with internal SOCs by providing continuous expert monitoring, AI-enhanced threat detection, automated response actions, and compliance support within a manageable service agreement. It suits the limited resources typical of local government IT teams.
Q: How does AI-native technology enhance MDR services for the public sector?
A: AI-native technology integrates artificial intelligence throughout detection, investigation, and response rather than adding it as a standalone feature. It can correlate activity across endpoints, identities, email, networks, and cloud environments; investigate alerts using environmental context; prioritize credible threats; and recommend or execute approved response actions. This reduces manual triage and helps lean public-sector security teams detect and contain threats faster. AI should complement—not replace—human expertise.
Q: Which security and compliance requirements should state and local agencies discuss with an MDR provider?
A: The requirements depend on the agency’s responsibilities, jurisdiction, systems, and the types of data the MDR provider will access. No single MDR service automatically “covers” public-sector compliance, so agencies should first identify which requirements apply and then determine how the provider will support them.
Q: Is it possible to integrate MDR with existing government IT systems?
A: Yes, leading MDR platforms offer extensive integrations with existing networks, cloud infrastructures, endpoints, and SaaS applications, providing comprehensive security coverage and operational cohesion.