Coro and AgileBlue both offer unified cybersecurity platforms designed to reduce the workload placed on lean IT and security teams. Both use artificial intelligence to correlate security activity, automate routine work, and respond to threats across multiple areas of the environment.
The more useful comparison is how each platform combines security operations, managed response, vulnerability and exposure management, human support, and strategic guidance. AgileBlue delivers these capabilities through an AI-native SecOps platform backed by a 24/7 U.S.-based SOC and Strategic Advisory Group. Coro provides a modular, AI-powered platform covering endpoint, email, cloud applications, identity, network, and data security, with managed service capabilities available through applicable packages and channel partners.
Buyers should compare what is included in each proposed package, which response actions happen automatically, how analysts become involved, and which operational responsibilities remain with the internal team.
AgileBlue vs. Coro for Mid-Market Cybersecurity
The two platforms address mid-market security needs through different operating models, so buyers should compare operational depth rather than feature counts. AgileBlue combines broad monitoring, proprietary orchestration, risk visibility, incident response, and strategic advisory services through an AI-native SecOps platform.
The following table presents our documented capabilities alongside questions buyers should ask Coro. These questions avoid assumptions about features, response authority, or services that may vary by package.
| Evaluation Area | AgileBlue’s Approach | Questions to Ask |
|---|---|---|
| Core model | AI-native SecOps supported by human cybersecurity specialists | Is the proposed package a consolidated product suite, a managed security operation, or both? |
| Monitoring | 24/7 monitoring across endpoint, network, cloud, application, Kubernetes, and API environments | Which environments receive continuous monitoring under the quoted package? |
| Response | AI-Native SecOps and 24/7 incident response | Which containment actions are included, and which require customer approval? |
| Risk visibility | Internal and external attack-surface scanning, risk scoring, and prioritized remediation | How are vulnerabilities, identities, assets, and external exposures correlated? |
| Vulnerability management | Continuous asset discovery, vulnerability scanning, and actionable remediation pathways | Is scanning continuous, and can the service discover previously unknown assets? |
| Strategic support | Maturity assessments, tabletop exercises, ongoing advisory support, and roadmap development | Are advisory services included, separately packaged, or unavailable? |
| Deployment | Cloud-based platform with vulnerability agents or network sensors available | What agents, connectors, infrastructure, or appliances are required? |
| Human access | U.S.-based cybersecurity experts and direct customer support | Can customers reach analysts directly during active investigations? |
A product demonstration should show one alert moving from detection through investigation and remediation. Ask both vendors to use the same scenario, such as a compromised Microsoft 365 account or an unknown device joining the network. A shared scenario makes workflow, escalation, and response differences easier to identify.
Coro Alternative for AI-Native SecOps
A credible Coro alternative should unite security data, automated decision-making, and human expertise within one operating model. We built our AI-powered security orchestration, automation, and response technology to coordinate security activity across endpoints, networks, and cloud environments.
This architecture reduces dependence on disconnected add-ons. Proprietary algorithms correlate relevant security data, analyze threats, and automate suitable response actions while presenting critical findings to analysts and customers. Automation does not remove people from security operations. It reserves their time for decisions that require business context and judgment.
Buyers comparing AI-native SecOps platforms should request specific evidence during evaluation:
- Ask the vendor to trace one incident across endpoint, identity, network, and cloud telemetry.
- Request the median time from detection to analyst review for critical alerts.
- Confirm which actions are autonomous, analyst-led, customer-approved, or excluded.
- Review a sample executive report and technical incident report before signing.
- Obtain written retention periods for logs, investigation records, and audit evidence.
- Ask whether response authority changes outside standard business hours.
The platform also extends visibility beyond the perimeter. Threat exposure management monitors compromised identities, exposed credentials, stealer logs, malicious domains, brand impersonation, supply-chain exposure, and external attack-surface risk. AI-driven decisioning prioritizes these findings using business context before remediation begins.
24/7 Cybersecurity Monitoring and Incident Response
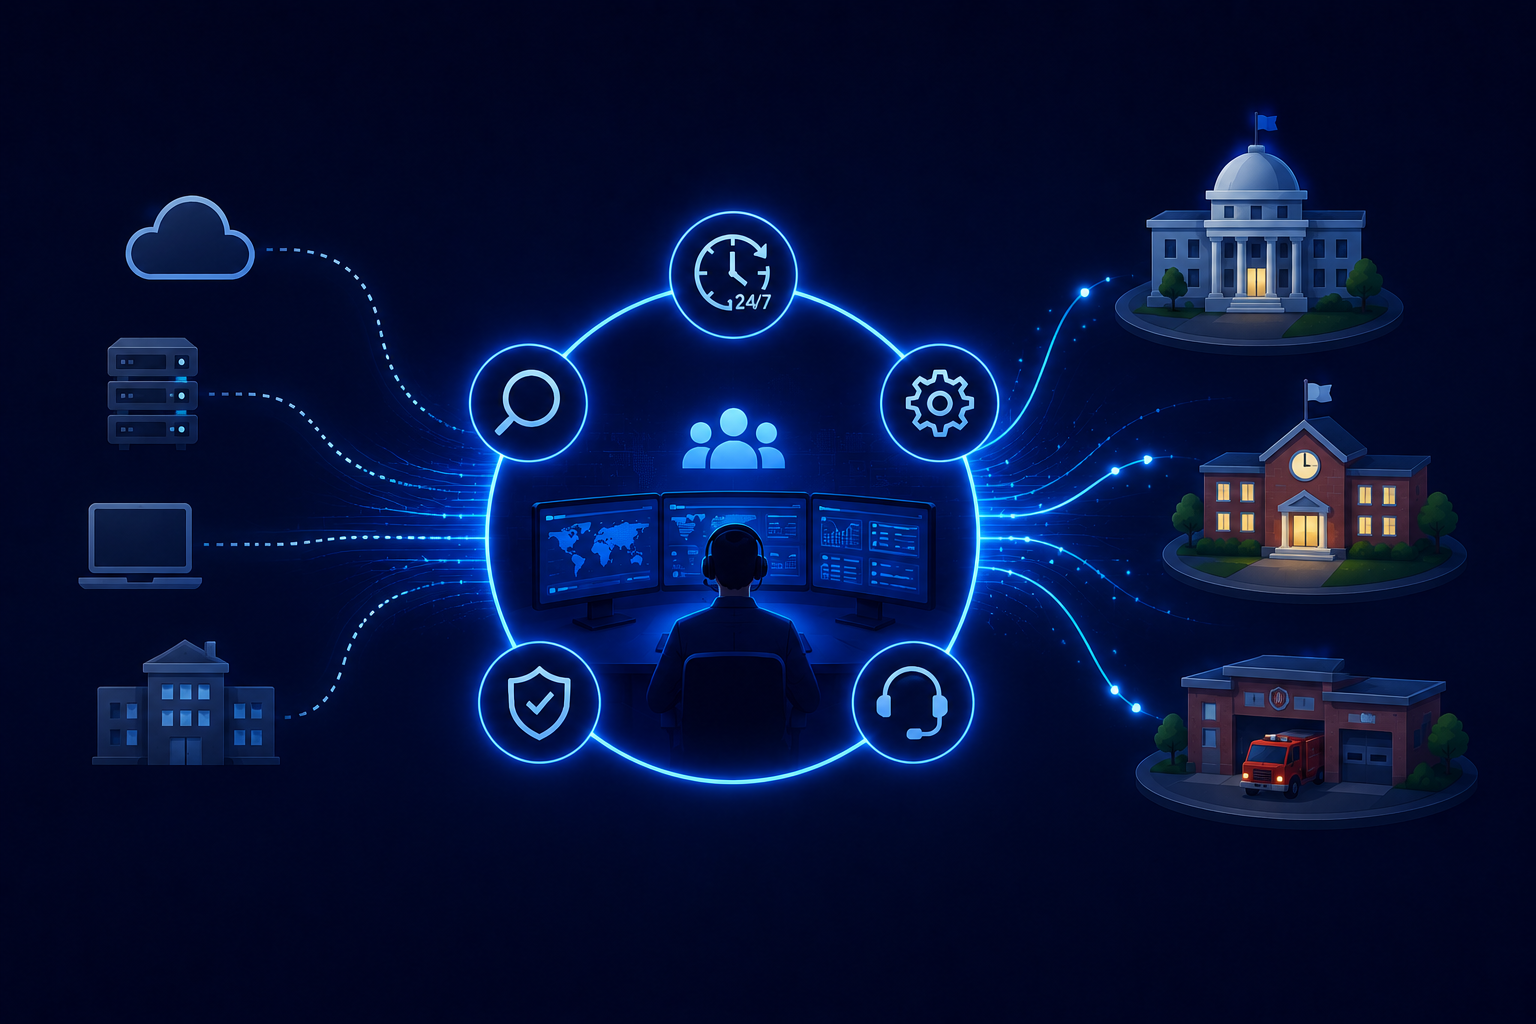
Effective 24/7 cybersecurity monitoring connects detection with investigation, escalation, containment, and documented follow-through. Our platform combines continuous monitoring with autonomous response technology and human support, giving mid-market teams an operating model designed for real incidents.
Before selecting a provider, ask for its escalation matrix. The document should identify severity levels, notification methods, response targets, decision authority, and after-hours contacts. A general promise of continuous monitoring does not reveal whether anyone can contain a compromised endpoint at 2:00 a.m.
Mid-sized businesses should evaluate these core requirements:
- Continuous security operations: Coverage should extend beyond business hours and include documented escalation procedures.
- Broad telemetry: Monitoring should cover endpoints, networks, cloud services, applications, Kubernetes environments, and APIs where applicable.
- AI-assisted correlation: Automation should connect related signals and reduce repetitive analyst work rather than create another alert queue.
- Actionable risk visibility: Vulnerabilities and exposures should be prioritized using identity, asset, and business context.
- Human support: Buyers should know whether experienced analysts are available during an active incident.
- Strategic guidance: Security maturity assessments, tabletop exercises, and roadmaps should connect technical work with business priorities.
Coverage can extend across endpoints, networks, cloud infrastructure, applications, Kubernetes, and APIs. Integrated vulnerability intelligence and external exposure data allow analysts to evaluate an incident within a broader risk context rather than reviewing one isolated alert.
Vulnerability Management and Attack-Surface Visibility
Vulnerability management should continuously discover assets, identify weaknesses, prioritize remediation, and track risk reduction over time. AgileBlue partners with Nodeware for integrated vulnerability scanning that can run through device-level agents or a catch-all network sensor.
Dynamic asset discovery updates the inventory as devices appear. Real-time alerts identify new devices and newly detected vulnerabilities, including risks linked to overlooked Internet of Things equipment. Low network utilization allows scanning to run in the background without requiring a physical appliance.
Johnson Investment Counsel offers a measurable example. The financial firm expanded monitoring to Microsoft 365, Salesforce, and Duo, received automated reporting, and met weekly with a dedicated security analyst. It reported their cyber risk score moved from the 400s to above 900 after more accurate scanning exposed previously unknown risks and guided remediation.
When comparing vendors, request a sample vulnerability report containing at least one critical issue. Check whether it names the affected asset, explains exploitability, assigns ownership, recommends a fix, and records closure evidence. A severity label without a remediation workflow offers limited operational value.
Strategic Advisory and Compliance Support
Strategic advisory services convert technical findings into a prioritized security roadmap. Our Strategic Advisory Group gives organizations access to experienced security leaders for compliance planning, security maturity improvement, and incident preparation.
Available advisory capabilities include:
- Security maturity assessments with tailored improvement roadmaps
- Tabletop exercises that identify gaps in incident response plans
- Ongoing reviews as security programs and business requirements change
- Coordination with trusted digital forensics, incident response, and penetration-testing partners
- Integration of partner findings into the long-term security roadmap
This capability matters when an organization lacks an internal chief information security officer. A mid-sized business may have capable IT leadership but still require specialized support for governance, board reporting, regulatory examinations, or major incidents.
Ask whether advisory support is proactive or available only after an escalation. Request a proposed 12-month meeting schedule, named deliverables, and a sample maturity roadmap. These materials distinguish an ongoing strategic relationship from occasional consulting hours.
Compare Your Cybersecurity Options
We can demonstrate how our AI-native SecOps platform handles your requirements, from 24/7 monitoring to vulnerability remediation and executive reporting.
Request a tailored comparison to review coverage, response authority, integrations, advisory support, and migration priorities. Bring your current security stack or Coro proposal, and we will map the operational differences.
Frequently Asked Questions
Q: Can I replace several cybersecurity tools with one SecOps platform?
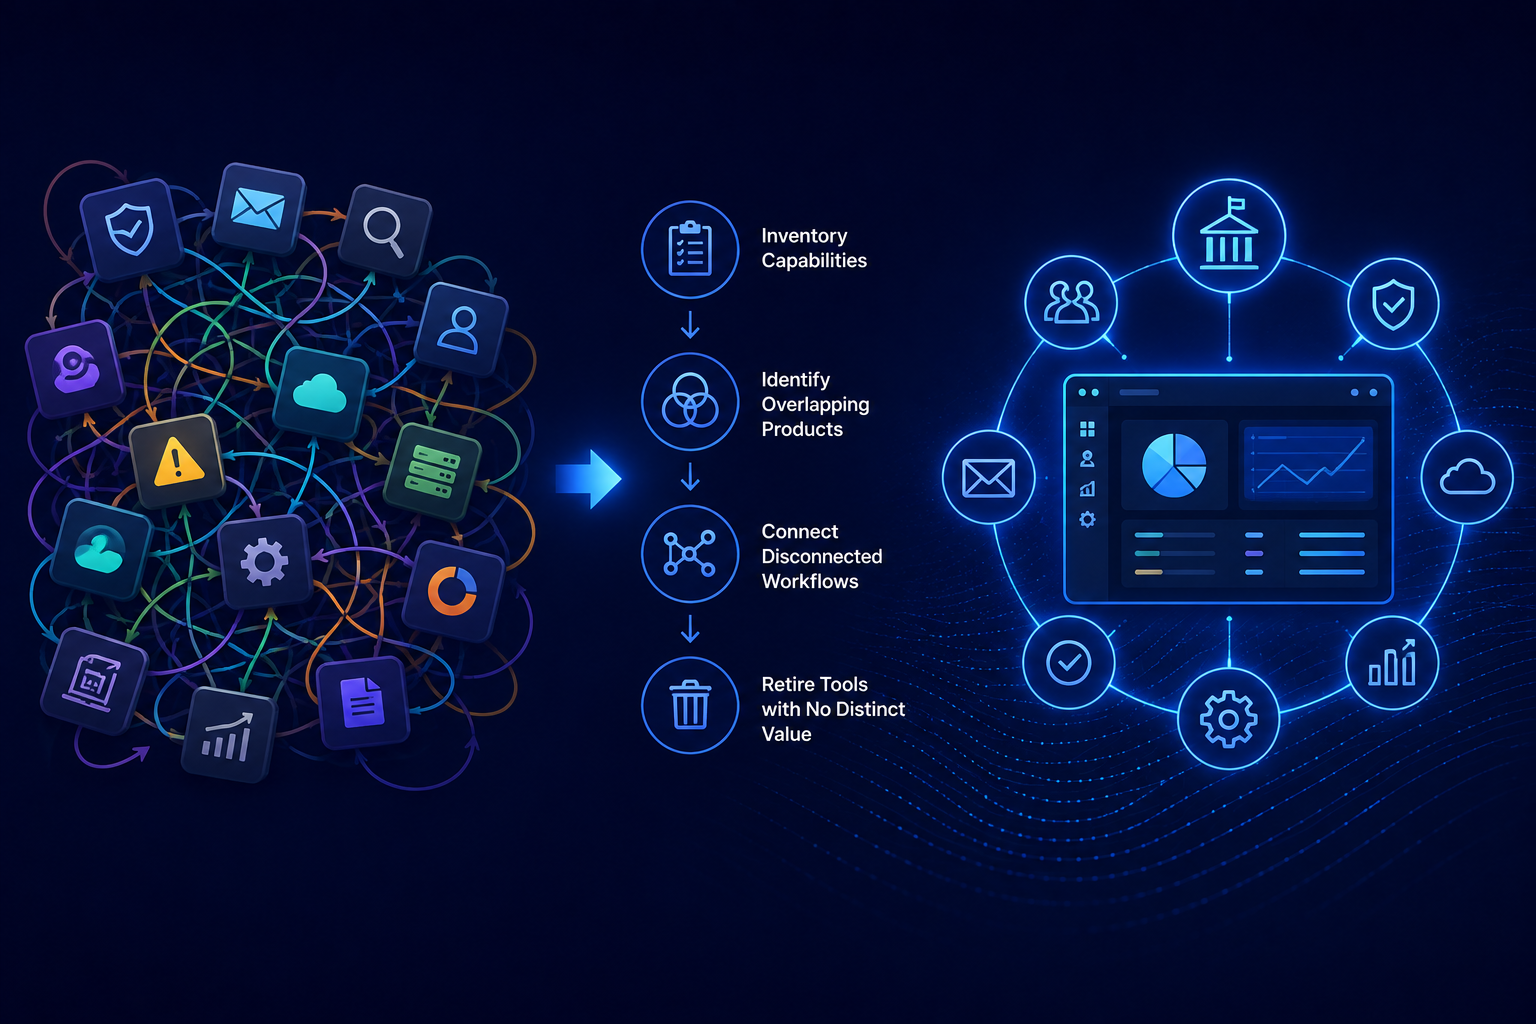
A: A unified SecOps platform can reduce tool sprawl when it covers the required endpoint, network, cloud, identity, vulnerability, and response functions. Create an inventory of current controls, then map each control to the new platform. Do not retire an existing tool until replacement coverage has been tested.
Q: How much internal security staff do I need with 24/7 managed monitoring?
A: Staffing needs depend on the provider’s response authority and your regulatory obligations. A managed platform can reduce the need for overnight monitoring personnel, but your company still needs named owners for business decisions, account access, recovery priorities, and vendor coordination.
Q: What should I ask during a cybersecurity platform demo?
A: Ask the vendor to investigate a realistic incident from detection through containment. Request live views of alert correlation, raw telemetry, response actions, vulnerability prioritization, escalation records, executive reporting, and audit evidence. Confirm which demonstrated capabilities are included in the quoted package.
Q: How long does it take to switch cybersecurity platforms?
A: Migration time varies with the number of endpoints, cloud services, network segments, integrations, and compliance requirements. A responsible plan should include asset discovery, connector deployment, alert tuning, escalation testing, reporting validation, and an overlap period before the previous platform is retired.