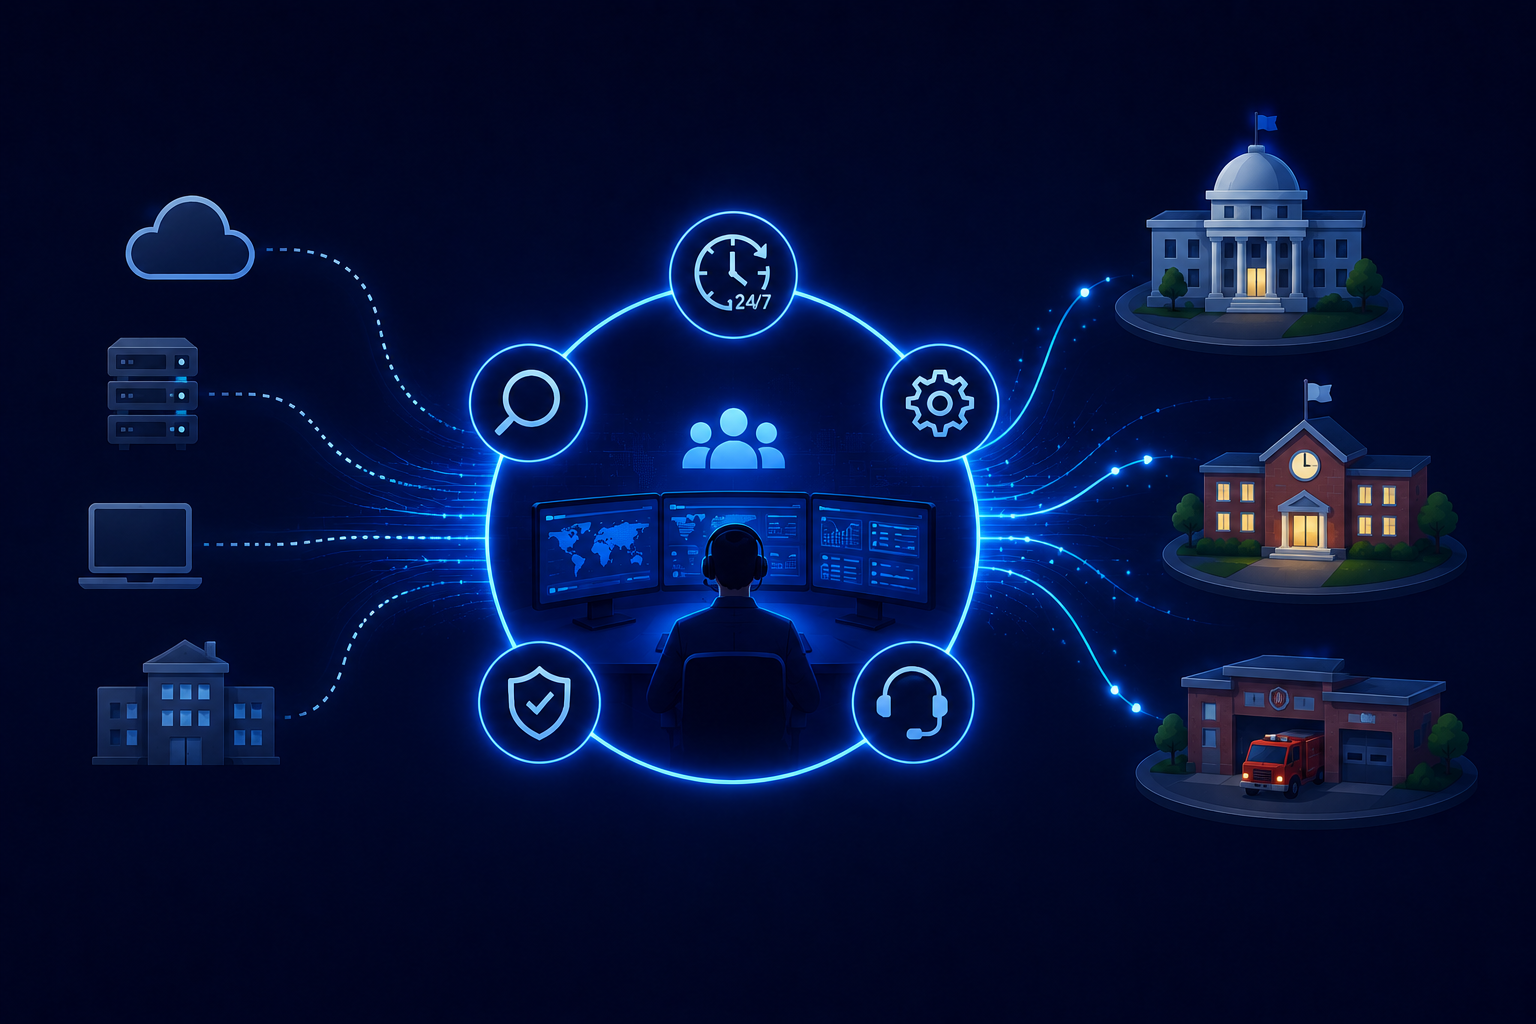
CrowdStrike and AgileBlue both combine agentic automation with 24/7 human security expertise, but they package and deliver those capabilities differently. CrowdStrike Falcon Complete provides managed detection, investigation, containment, and remediation through the broader Falcon platform, Charlotte AI, autonomous agents, and CrowdStrike analysts. AgileBlue delivers AI-native security operations through Sapphire AI and a U.S.-based SOC, with detection, investigation, and response configured around each customer’s environment and documented preferences. Mid-sized organizations should therefore compare the capabilities included in each service, the authority granted to automated response, the technologies that can be integrated or consolidated, the human support model, and how security performance is measured.
What is Traditional MDR and How Does It Work?
Traditional MDR providers combine SOC analysts, detection tools, and incident response processes to monitor client environments 24/7. Human experts analyze alerts generated by SIEM (Security Information and Event Management) systems and endpoint detection platforms, escalating and investigating suspicious activity.
While this approach leverages deep human judgment and expertise, it often faces challenges of high alert volume and analyst fatigue. SOCs face mounting alert overload. Verizon’s 2025 DBIR analyzed 22,052 security incidents, while separate research found analysts can receive thousands of alerts daily, with 45% reported as false positives. This noise can strain teams and delay threat detection.
The traditional model often requires clients to manage multiple security tools, integrate vendor solutions, and support data correlation efforts. Incident handling then depends heavily on SOC analysts’ manual triage and investigation workflows, which can introduce variability in response speed and accuracy.
Is CrowdStrike Still a Traditional, Human-Led MDR Provider?
No. CrowdStrike built its reputation on endpoint detection and response (EDR) through its Falcon platform, combined with a global human SOC team that manually triaged and investigated alerts. That changed with the introduction of Charlotte AI, the Charlotte AI AgentWorks ecosystem, and Charlotte Agentic SOAR. CrowdStrike also introduced Agentic MDR through its Falcon Complete managed service, where analysts now deploy AI agents to handle automated workflows rather than triaging every alert by hand.
Describing CrowdStrike today as a purely human-analyst, non-agentic platform is no longer accurate. The more useful framing for evaluating it against AgileBlue isn’t “human-led vs. AI-led,” it’s architectural: AI-native from inception, versus agentic AI capability layered onto an established endpoint-and-human-SOC model. That’s the distinction the rest of this comparison is built around.
How CrowdStrike Delivers Agentic MDR Through Falcon Complete
CrowdStrike Falcon Complete combines the Falcon platform, Charlotte AI, security automation, and 24/7 expert oversight to deliver managed detection, investigation, containment, and remediation. Although CrowdStrike established its reputation through endpoint security, Falcon Complete now extends beyond endpoints to provide visibility across identities, cloud workloads, network activity, email, SSO, and third-party security data through Falcon Next-Gen SIEM.
Within this model, Charlotte AI and CrowdStrike’s autonomous agents support alert triage, cross-domain investigation, attack correlation, and response orchestration. CrowdStrike analysts direct and validate critical decisions while performing full-cycle remediation, which may include isolating compromised systems, removing attacker persistence, and helping restore the environment to a known-good state.
The precise scope depends on the Falcon products, managed services, third-party data coverage, and response permissions included in the customer’s agreement. Mid-sized organizations should confirm which telemetry sources are covered, which capabilities require additional licensing, how much third-party data can be ingested and retained, which response actions CrowdStrike can perform autonomously, and what remediation responsibilities remain with the internal team.
How AI-Native SecOps Platforms Differ From Traditional MDR
AI-driven security platforms, often called AI-native SecOps, embed AI capabilities deeply into all aspects of detection and response. Rather than retrofitting AI atop existing tools, these platforms utilize machine learning, automation, and agentic AI to autonomously investigate incidents and even execute response actions without human intervention.
Key differentiators include:
- Native AI Architecture: AI is built into the platform’s core, enabling real-time automated analysis of diverse data sources across endpoints, cloud, and networks.
- Focus on Attack Chains: Instead of treating alerts in isolation, AI maps and prioritizes attacks across the kill chain, reducing noise and false positives.
- Reduced MTTD: Autonomous triage cuts detection time to minutes — industry data cites reductions from hours in traditional MDR to 4.6 minutes or less in leading AI platforms.
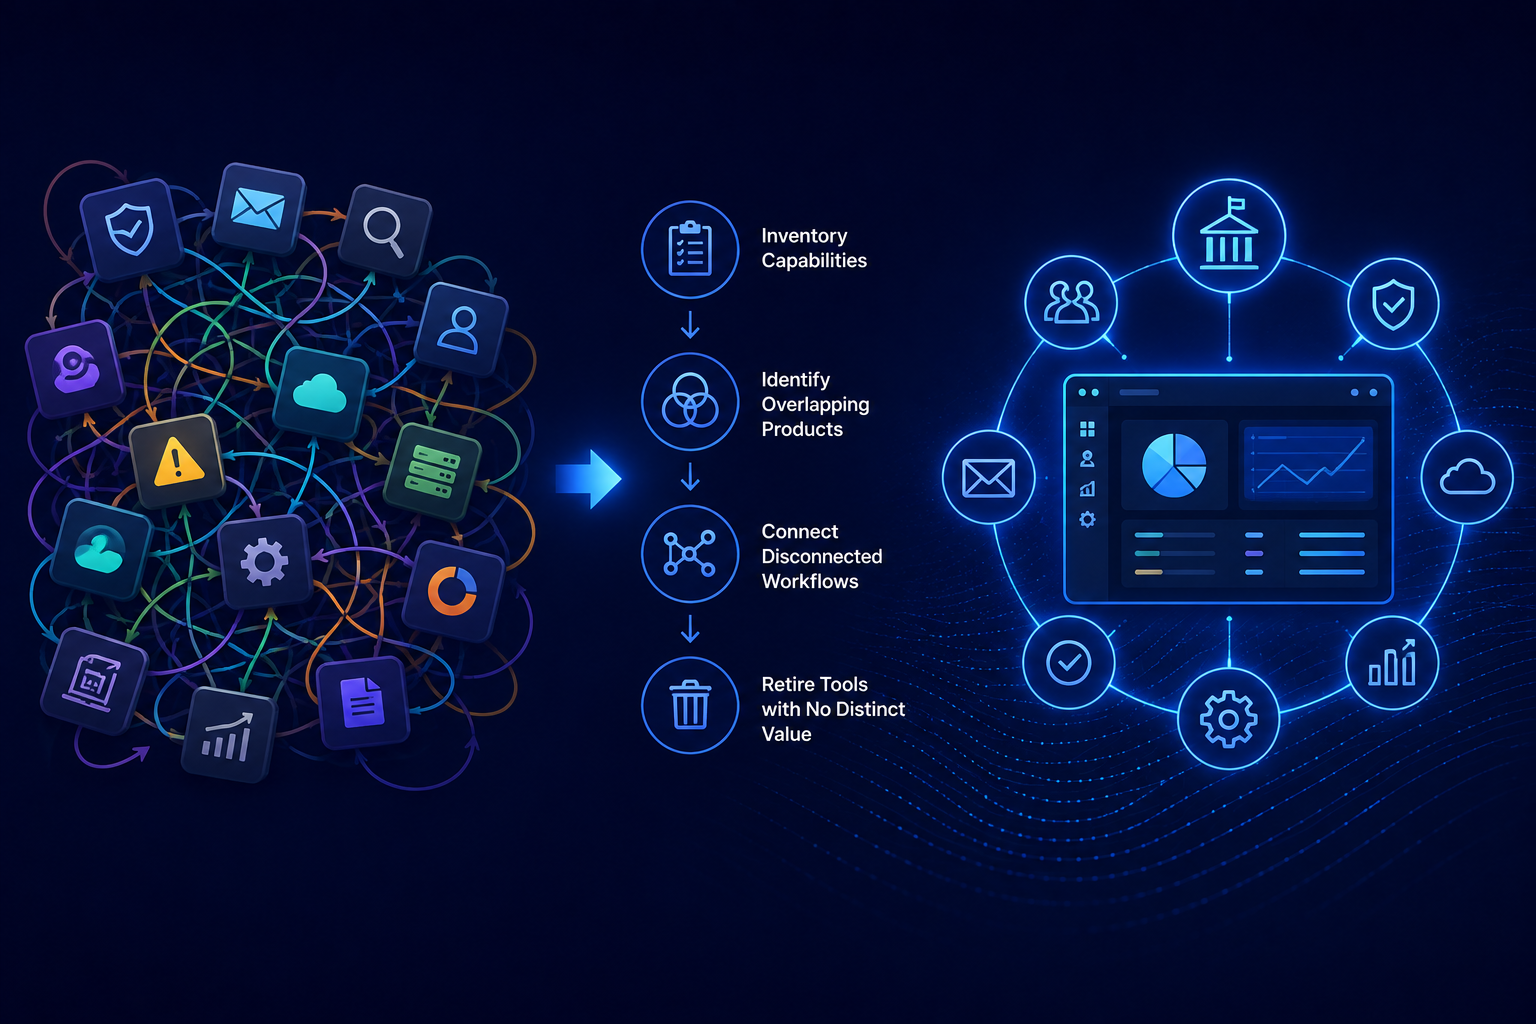
- Consolidation of Tools: AI platforms integrate SIEM, EDR/XDR, SOAR, vulnerability scanning, and more into unified workflows, simplifying management.
- Human-AI Collaboration: Experienced analysts validate AI-driven decisions and provide strategic oversight, helping governance and context.
What Should CIOs Look for in an MDR Provider?
Choosing an MDR provider requires assessing capabilities against organizational needs and security maturity. CIOs should consider:
- Detection and Response Speed: Evaluate average MTTD and MTTR metrics. Autonomous AI can reduce detection time significantly, but human oversight remains crucial for complex threats.
- False Positive Reduction: Platforms focused on attack chains and utilizing AI-driven correlation typically generate fewer false alerts, improving analyst efficiency.
- Operational Transparency: Providers should offer clear visibility into detection and response workflows, with robust reporting and customizable dashboards.
- Integration and Consolidation: A unified platform reduces tool sprawl and management overhead. Ask about native integrations and support for existing security investments.
- Human Expertise and Support: While AI accelerates operations, human experts provide critical judgment and strategic guidance. Assess the provider’s SOC team credentials and collaboration model.
- Scalability and Cost Predictability: Assess pricing models and platform scalability relative to organizational growth and compliance demands.
- Industry-Specific Experience: Providers with vertical experience (e.g., healthcare, manufacturing, public sector) better understand unique risks and regulatory requirements.
Mid-market organizations with lean security teams often benefit from platforms emphasizing automation and AI-native capabilities, allowing fewer analysts to handle greater workloads without sacrificing coverage.
| Evaluation | CrowdStrike Falcon + Charlotte AI | AgileBlue AI-Native SecOps |
| Operation Model | Expert-led, AI-powered MDR combining the Falcon platform, Charlotte AI, autonomous agents, deterministic automation, and a global team of analysts and threat hunters. | AI-native, human-supported SecOps combining Sapphire AI with a 24/7 U.S.-based SOC and dedicated customer support. |
| Platform Coverage | Provides native capabilities across endpoints, identities, cloud workloads, threat intelligence, exposure management, and other areas. Falcon Next-Gen SIEM extends visibility to network, email, SSO, SaaS, and third-party security data. | Correlates activity across endpoints, identities, email, networks, cloud environments, SaaS applications, and other connected technologies. The platform also includes cloud security, vulnerability management, threat exposure management, M365 security, and Shadow AI monitoring. |
| AI Investigation | Charlotte AI and CrowdStrike agents support detection triage, cross-domain correlation, investigation, contextual analysis, and response orchestration. | Sapphire AI continuously correlates activity, investigates suspicious behavior, prioritizes credible incidents, and closes cases determined to be benign. |
| Tool Integration | Can consolidate multiple security functions within Falcon while ingesting third-party data through Next-Gen SIEM. Available integrations, ingestion limits, retention, and managed coverage depend on licensing and service selection. | Brings multiple security capabilities into one operating environment while supporting hundreds of integrations. Buyers should confirm which existing products can be retained, replaced, or retired. |
| Human Involvement | CrowdStrike analysts direct and validate agents, own critical decisions, conduct threat hunting, and execute remediation from detection through resolution. | AgileBlue analysts provide continuous oversight and handle complex, ambiguous, or high-impact incidents requiring additional context and human judgment. |
| Support Model | Global SOC coverage supported by CrowdStrike analysts, threat hunters, threat intelligence, and incident-response expertise. | 24/7 U.S.-based SOC support, dedicated customer success, and access to broader Strategic Advisory services. |
| Potential Fit | May fit organizations seeking a large-scale security ecosystem, deep endpoint expertise, global threat intelligence, and broad enterprise platform capabilities. | May fit mid-sized organizations seeking configurable autonomous response, platform consolidation, measurable detection and response performance, and a white-glove support model designed for lean teams. |
Why AI-Driven SecOps Is Gaining Traction
Industry analysts emphasize that AI-driven platforms address critical pain points facing mid-market security teams: alert fatigue, talent shortages, and fragmented tool stacks. By aligning detection with the attack lifecycle and enabling autonomous responses, these solutions enable lean teams to operate with enterprise-grade effectiveness.
A 2025 Forrester Consulting study found that Google SecOps, leveraging generative AI and automation, reduced mean time to investigate by 50% and mean time to respond by 65%, while enabling junior analysts to take on 35% more SecOps work. This aligns closely with mid-market CIOs’ priorities to secure environments without hiring large teams or deploying overly complex solutions.
Why Consider AgileBlue as an AI-Native SecOps Option
AgileBlue exemplifies the AI-native SecOps approach with a platform built from the ground up to automate large portions of Tier 1 and Tier 2 analyst work, auto-close benign cases, and reduce MTTD to 4.6 minutes. The platform consolidates multiple key security operations—including SIEM, EDR/XDR, SOAR, vulnerability scanning, and cloud security—into one unified platform designed for mid-sized organizations with lean IT teams.
Backed by 24/7 expert analysts who validate AI-driven decisions, AgileBlue provides a balance of autonomous operations with human oversight, reducing noise and operational silos. Their white-glove collaborative SOC model also fosters partnership with customer teams.
While AgileBlue represents one of several AI-native MDR options, mid-market organizations evaluating alternatives to larger enterprise providers like CrowdStrike should assess how AI-native platforms might align with their need for speed, efficiency, and scalability.
Schedule Your Consultation With Our Security Experts
Navigating the MDR provider landscape can be challenging amid evolving threats and operational constraints. We invite CIOs and IT leaders to explore how AgileBlue’s approach compares to CrowdStrike’s Falcon platform in detail to find the right balance for their security strategy.
Our team offers expert consultations that analyze your current posture and plans to recommend solutions that reduce alert fatigue, accelerate response times, and consolidate your security tools efficiently. Contact us today to discuss your unique needs and explore how AI-driven security platforms could transform your MDR experience.
FAQ
Q: Does CrowdStrike use agentic AI, or is it purely endpoint-and-human-analyst?
A: CrowdStrike’s Charlotte AI ecosystem adds agentic automation to its Falcon platform, and Agentic MDR extends this into its managed service. It is not a purely human-driven model, the comparison with AI-native platforms now centers on where automation sits in the workflow, not whether it exists.
Q: How does AgileBlue differ from CrowdStrike’s Charlotte AI-enabled Falcon platform?
A: The distinction is architectural. AgileBlue was built with automation as the foundation across endpoints, cloud, network, and identity from day one; CrowdStrike’s Charlotte AI adds agent-driven automation onto an established endpoint-centric platform. Both reduce manual workload, but the balance of automated vs. human-reviewed decisions should be confirmed directly with each vendor.
Q: Can AI-driven platforms fully replace human analysts?
A: No. Both CrowdStrike’s model and AgileBlue’s platform retain human analysts for governance, complex incidents, and high-stakes decisions, AI accelerates and automates routine work rather than replacing expert judgment.
Q: What should CIOs prioritize when evaluating MDR providers?
A: Detection speed backed by verifiable figures, real automation depth (not just AI presence), integration breadth, human oversight structure, scalability, cost predictability, and vertical-specific experience.