What Are the Best Cybersecurity Strategies for Higher Education to Prevent Ransomware Attacks?
Higher education institutions face unique cybersecurity challenges, with ransomware remaining one of the most significant threats. The best cybersecurity strategies combine robust prevention, continuous monitoring, effective incident response, and resilience-building tailored to the academic environment. A layered, proactive approach is critical to safeguarding campuses today.
Higher education institutions operate complex and open IT environments that make them attractive ransomware targets. Sensitive research data, student records, and operational systems are at risk. The diversity of users and devices within universities broadens the attack surface, while budget constraints and legacy systems can exacerbate vulnerabilities. Understanding this context helps build cybersecurity strategies that are both effective and practical.
How Can Colleges and Universities Build Resilience Against Ransomware?
Colleges and universities can build resilience against ransomware by adopting a multifaceted framework centered on prevention, detection, and recovery.
First, prevention focuses on hardening defenses to reduce ransomware infection risk. This involves applying rigorous patch management to close known software vulnerabilities and deploying endpoint detection and response (EDR) tools to identify suspicious activity early. According to Sophos’ State of Ransomware in Education 2025 survey, 58% of higher education organizations experienced a ransomware attack that resulted in data encryption over the previous year, underscoring the continued need for proactive cybersecurity measures.
Second, continuous monitoring of network activity using Security Information and Event Management (SIEM) enables organizations to detect ransomware behavior patterns rapidly. Behavioral analytics and AI-driven tools improve detection accuracy, helping to differentiate true threats from benign anomalies. This ongoing vigilance shortens dwell time before a response, reducing potential damage.
Third, incident response plans must be comprehensive and well-tested. Effective strategies include predefined roles, communication pathways, and containment procedures. Regular tabletop exercises prepare staff for cyber incident scenarios, minimizing confusion when attacks occur.
Finally, resilience depends heavily on data protection practices. Regular, immutable backups stored offline or in geographically isolated locations allow institutions to restore systems without paying ransoms.
Building cybersecurity maturity also involves staff education programs to reduce ransomware phishing and social engineering’s effectiveness, two primary infection vectors. Tailored awareness campaigns that mimic real-world attacks improve users’ ability to identify suspicious emails.
What Are the Most Effective Ways to Protect Higher Education Institutions from Ransomware?
The most effective ransomware protection strategies for higher education combine technical, procedural, and cultural measures:
- Adopt a Zero Trust Architecture: Implementing a Zero Trust approach helps limit attackers’ ability to move laterally if a system is compromised. Rather than assuming trust based on network location, Zero Trust combines explicit verification, least-privilege access, device and identity context, network segmentation, and continuous evaluation of access decisions. For higher education institutions with open and distributed network environments, this layered approach significantly strengthens overall network security.
- Implement Multi-Factor Authentication (MFA): Enforcing MFA across all critical systems drastically reduces the risk of credential compromise, a common ransomware infection vector.
- Automate Threat Detection and Response: Incorporating AI-powered security orchestration and automation platforms enables rapid identification and autonomous remediation of ransomware behaviors. This automated response can isolate infected systems before widespread impact.
- Conduct Regular Security Assessments: Penetration testing simulates attack scenarios, revealing weaknesses for remediation before adversaries exploit them.
- Collaborate Within Sector Partnerships: Engaging in information sharing through entities like the REN-ISAC or regional Information Sharing and Analysis Centers (ISACs) helps institutions stay abreast of emerging threats and best practices.
- Maintain Compliance with Regulations: Aligning security programs with standards such as HIPAA (for healthcare-related research data) reinforces rigorous controls and accountability.
- Resource Planning: Designating budgets and staff dedicated to cybersecurity sustains continuous program improvement and operational resilience.
Why AgileBlue’s Approach Exemplifies Best Practices
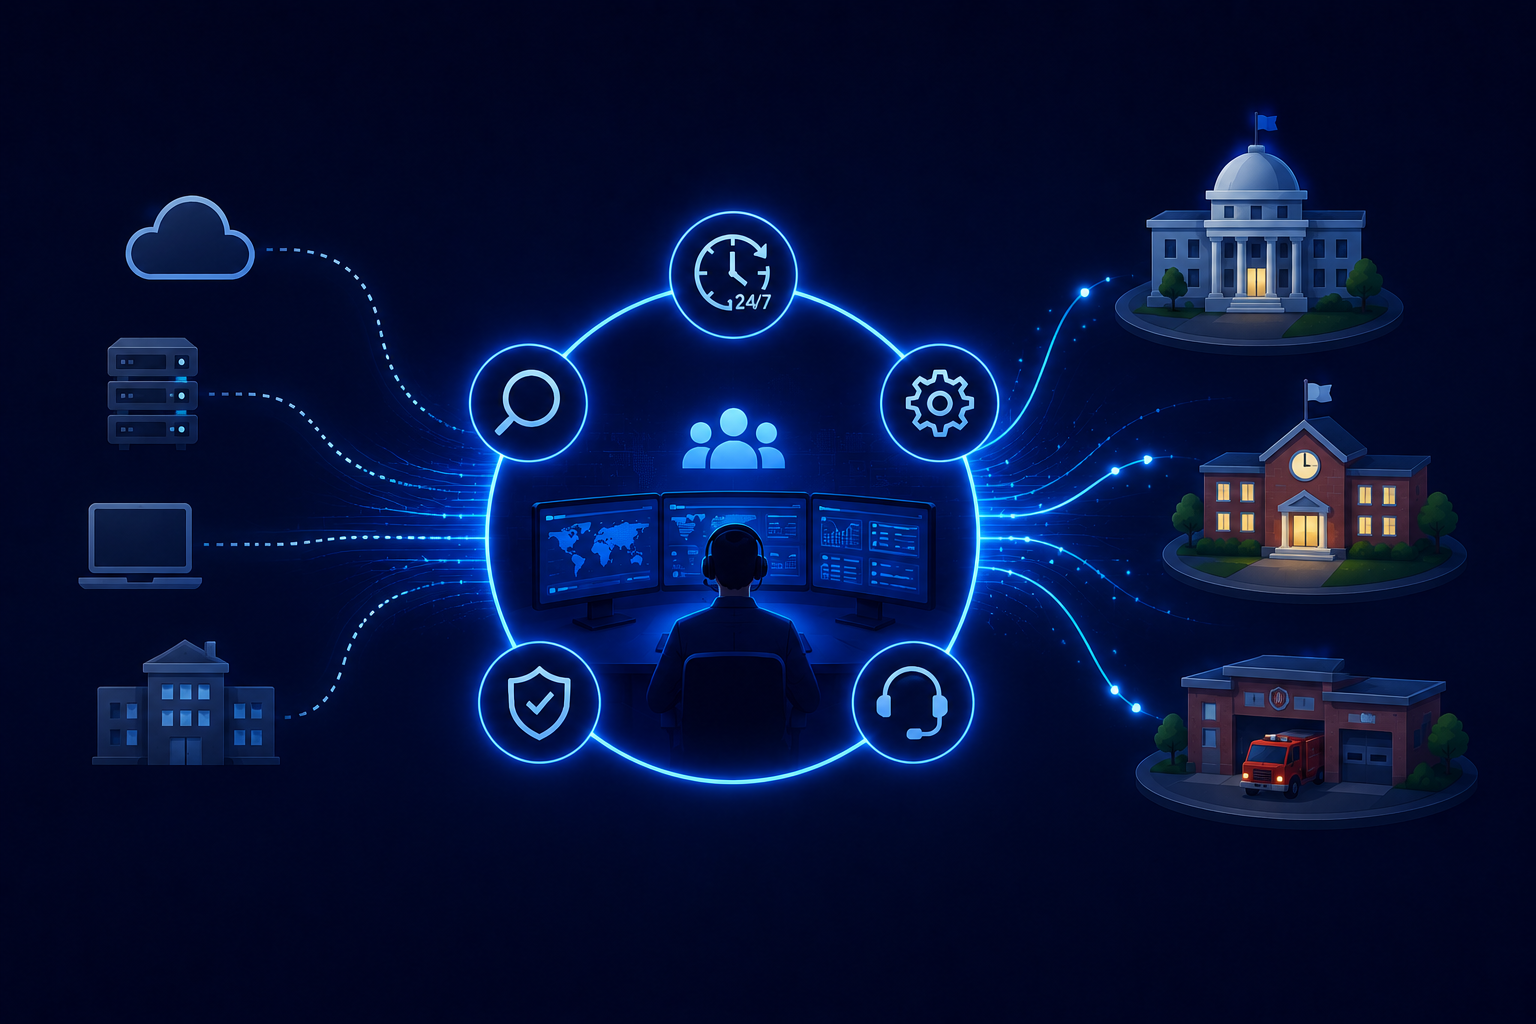
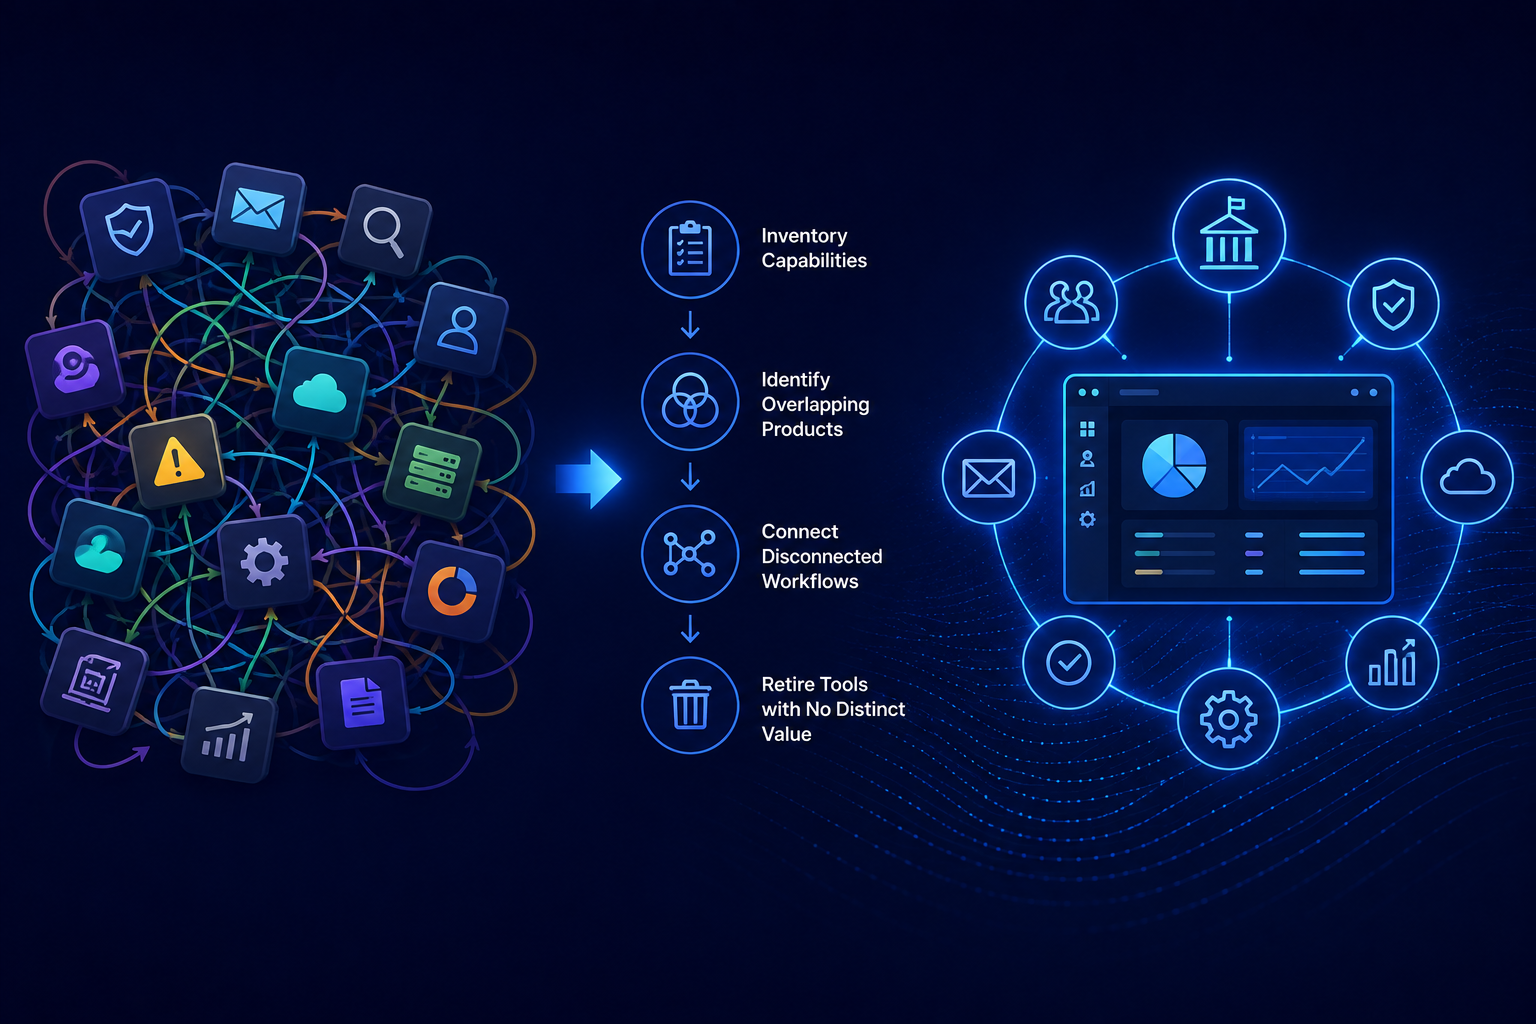
For colleges and universities that cannot staff and operate a full in-house SOC, AgileBlue provides 24/7 detection, investigation, and response across complex IT environments. Its AI-native SecOps platform connects activity across endpoints, identities, email, networks, and cloud environments, helping lean security teams identify related threats without manually working through disconnected alerts.
Sapphire AI continuously investigates suspicious activity and makes response decisions in real time based on each institution’s defined response preferences. Routine threats can be addressed autonomously, while U.S.-based SOC analysts respond when an incident requires human judgment. This combination has helped AgileBlue achieve a mean time to detect of 4.6 minutes while allowing customers to maintain control over how incidents are handled.
AgileBlue should serve as one component of a broader resilience strategy—not a replacement for strong identity governance, network segmentation, tested backups, incident-response planning, and security awareness. By combining AI-driven speed with experienced human support, AgileBlue helps higher-education teams strengthen around-the-clock protection without significantly increasing internal headcount.
Schedule a Consultation to Strengthen Your Cybersecurity Resilience
Higher education institutions must act decisively to combat ransomware threats with comprehensive and context-aware cybersecurity strategies. A thorough assessment of your current security posture, adoption of layered defenses, and investment in continuous monitoring and rapid response capabilities form the foundation of effective defense.
Partnering with experienced cybersecurity providers who offer AI-enhanced detection and expert SOC support, such as AgileBlue, can complement internal efforts while adapting to the unique needs of academic environments. Together, these strategies create robust defenses to safeguard your institution’s mission and data integrity.
Frequently Asked Questions
Q: What makes ransomware attacks particularly dangerous for higher education institutions?
A: Universities manage sensitive personal data, proprietary research, and critical operational systems, which are valuable targets. Their open networks, diverse device usage, and decentralized IT create vulnerabilities that ransomware exploits to lock systems and demand ransoms, causing significant disruption and damage.
Q: How often should backups be performed to protect against ransomware?
A: Backup frequency should be based on the institution’s recovery point and recovery time objectives, with critical systems backed up more frequently than lower-priority systems. Backups should be immutable or offline, logically isolated from production systems, protected with separate administrative credentials, and regularly tested to confirm that data and services can be restored successfully.
Q: Are AI and automation necessary for effective ransomware defense in higher education?
A: AI-driven detection and automated response tools provide significant advantages by quickly identifying threats and reducing workload on security teams. Automation enables institutions to contain incidents promptly, which is essential in environments affecting many users.
Q: Can security awareness training significantly reduce ransomware infection risk?
A: Security awareness training can reduce the likelihood that phishing, credential theft, and other social-engineering tactics lead to an incident, but training alone cannot prevent ransomware. Effective programs go beyond annual courses by providing continuous, role-specific education, realistic simulations, and simple ways for faculty, staff, and students to report suspicious activity quickly. Institutions should measure changes in reporting and user behavior—not merely training completion—and pair education with phishing-resistant MFA, email security, least-privilege access, endpoint protection, and 24/7 monitoring and response.
Q: How does implementing Zero Trust benefit higher education cybersecurity?
A: Zero Trust reduces risk by eliminating implicit trust based on a user’s location or connection to the campus network. Instead, access decisions consider identity, device health, requested resources, and current risk while enforcing least-privilege permissions. This is especially valuable in higher education, where students, faculty, researchers, contractors, and unmanaged devices routinely access decentralized systems. When combined with strong identity controls and network segmentation, Zero Trust helps preserve necessary academic access while limiting lateral movement and reducing the potential impact of a compromised account or device.