What Cybersecurity Tools Actually Reduce SOC Workload?
The Security Operations Center (SOC) workload is driven predominantly by the volume of alerts analysts must investigate, which often includes many false positives and low-priority events. Tools designed to cut this workload aim to automate alert triage, reduce noise, and enable faster response to critical threats.
Commonly used tools that reduce SOC workload include:
- Extended Detection and Response (XDR) and Endpoint Detection and Response (EDR): These tools collect and correlate data from multiple sources to give broader context around threats. However, they can still overwhelm analysts if alert fatigue is not addressed.
- Security Orchestration, Automation, and Response (SOAR): SOAR platforms automate repetitive security tasks such as data enrichment and case management, speeding up investigation workflows.
- AI-assisted investigation layered onto a human-led model: Providers like Huntress pair endpoint and identity telemetry with an Agentic Security Platform that handles investigation legwork, context gathering, signal correlation, and timeline building, while human analysts and threat hunters retain the final call on every verdict and response.
- AI-native SecOps platforms: Built from the ground up with AI, platforms like AgileBlue combine threat detection, investigation, and autonomous response into a unified system, automating a larger share of Tier 1/Tier 2 triage before a human reviewer is looped in.
Notably, autonomous response capabilities reduce Mean Time to Detect (MTTD) and Mean Time to Respond (MTTR) by automatically taking pre-approved actions during an attack, freeing analysts to focus on more strategic work. The distinction between the last two categories above isn’t whether AI is present, it’s how much of the investigation happens before a human is brought in, and that’s the comparison the rest of this piece walks through.
Comparing Huntress and AgileBlue
Huntress and AgileBlue both combine agentic AI, automation, and 24/7 human security expertise. Neither operates as a purely manual MDR service, and neither removes people from security operations entirely. The meaningful differences are how each platform governs autonomous investigations, which security data it brings together, which response actions it can perform, and when human analysts become involved.
Huntress describes its model as AI-centric and human-led. Its Athena investigation system uses more than 40 specialized AI agents to gather evidence, correlate signals, follow structured playbooks, and reach conclusions. Athena can complete certain well-defined, high-confidence investigations and deliver an incident report without human review. Complex, ambiguous, novel, and high-impact cases are transferred to Huntress analysts, who also establish Athena’s playbooks, thresholds, and guardrails.
AgileBlue describes its model as AI-native and human-supported. Sapphire AI continuously correlates activity across the environment, investigates suspicious behavior, closes cases determined to be benign, and initiates approved response actions according to each customer’s documented preferences. AgileBlue’s 24/7 U.S.-based SOC analysts handle situations requiring additional context, complex investigation, or human judgment.
| Aspect | Huntress Agentic Security Platform | AgileBlue AI-Native SecOps |
| Operating Model | AI-centric and human-led. AI performs substantial investigation work while analysts oversee the operating model and handle cases requiring human expertise. | AI-native and human-supported. Sapphire AI operates across detection, investigation, decision-making, and approved response, backed by 24/7 SOC analysts. |
| AI Investigation | Athena bundles related signals, collects evidence, builds timelines, follows structured playbooks, and can complete certain high-confidence investigations without human review. | Sapphire AI correlates related activity, investigates potential threats, prioritizes credible incidents, and closes cases determined to be benign. |
| Customer Control | Automated remediation can be enabled or disabled, and customers should confirm which response permissions apply to each Huntress service. | Customers define which actions Sapphire AI may execute autonomously, which require SOC analyst involvement, and which remain with the internal team. |
| Potential Fit | May fit organizations seeking managed endpoint, identity, log, and human-risk protection to agentic investigation and human-led SOC operating model. | May fit lean teams seeking broad cross-environmental correlation, configurable autonomous response, measurable detection and response performance, and unified security operations. |
Both providers can remove substantial work from an internal security team. Buyers should not base the decision solely on labels such as “AI-centric,” “human-led,” or “AI-native.” They should validate which investigations can be completed autonomously, which response actions are included, how customer approval is handled, what telemetry is supported, and how performance is measured.
Why Full Attack Chain Visibility Matters
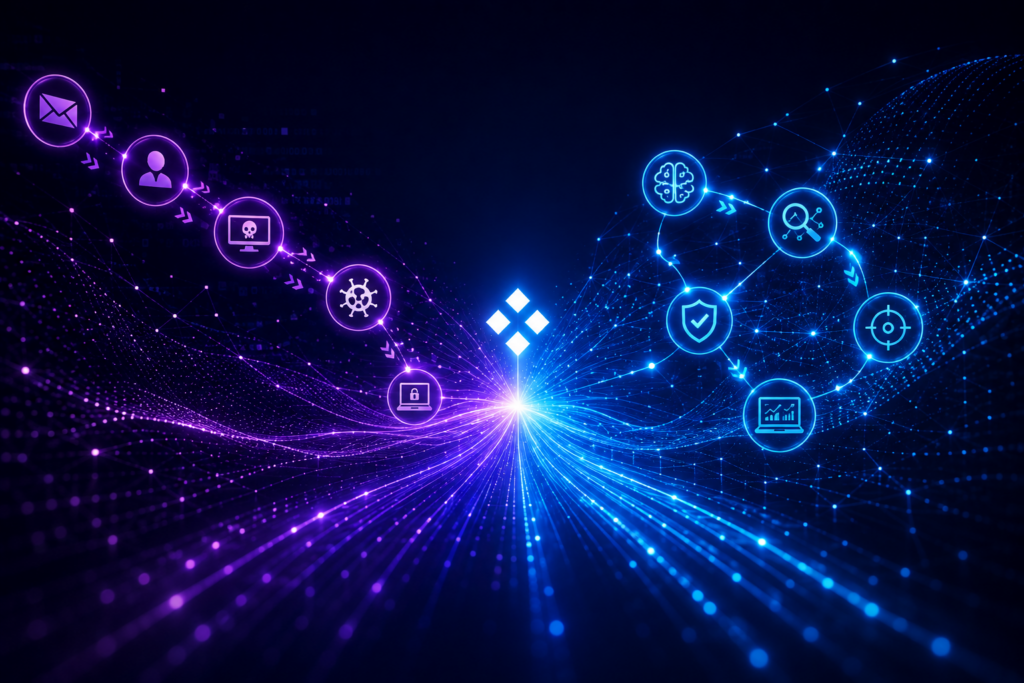
Attack chain detection is critical because threats rarely manifest as isolated endpoint events. Instead, attackers move through multiple phases, exploiting vulnerabilities across systems and networks. Huntress’s Agentic Security Platform correlates signals within its endpoint and identity telemetry; AgileBlue extends that correlation further, across network and cloud activity as well. Without visibility into the full chain, SOC analysts may miss indicators of compromise or respond too late to contain damage.
Practical Recommendations for Simplifying Security Operations
Organizations looking to reduce SOC workload without increasing headcount can consider the following approaches:
1. Evaluate AI-Native Platforms: Choose platforms built with AI from inception, focusing on autonomous response features that automate routine Tier 1 and Tier 2 analyst tasks.
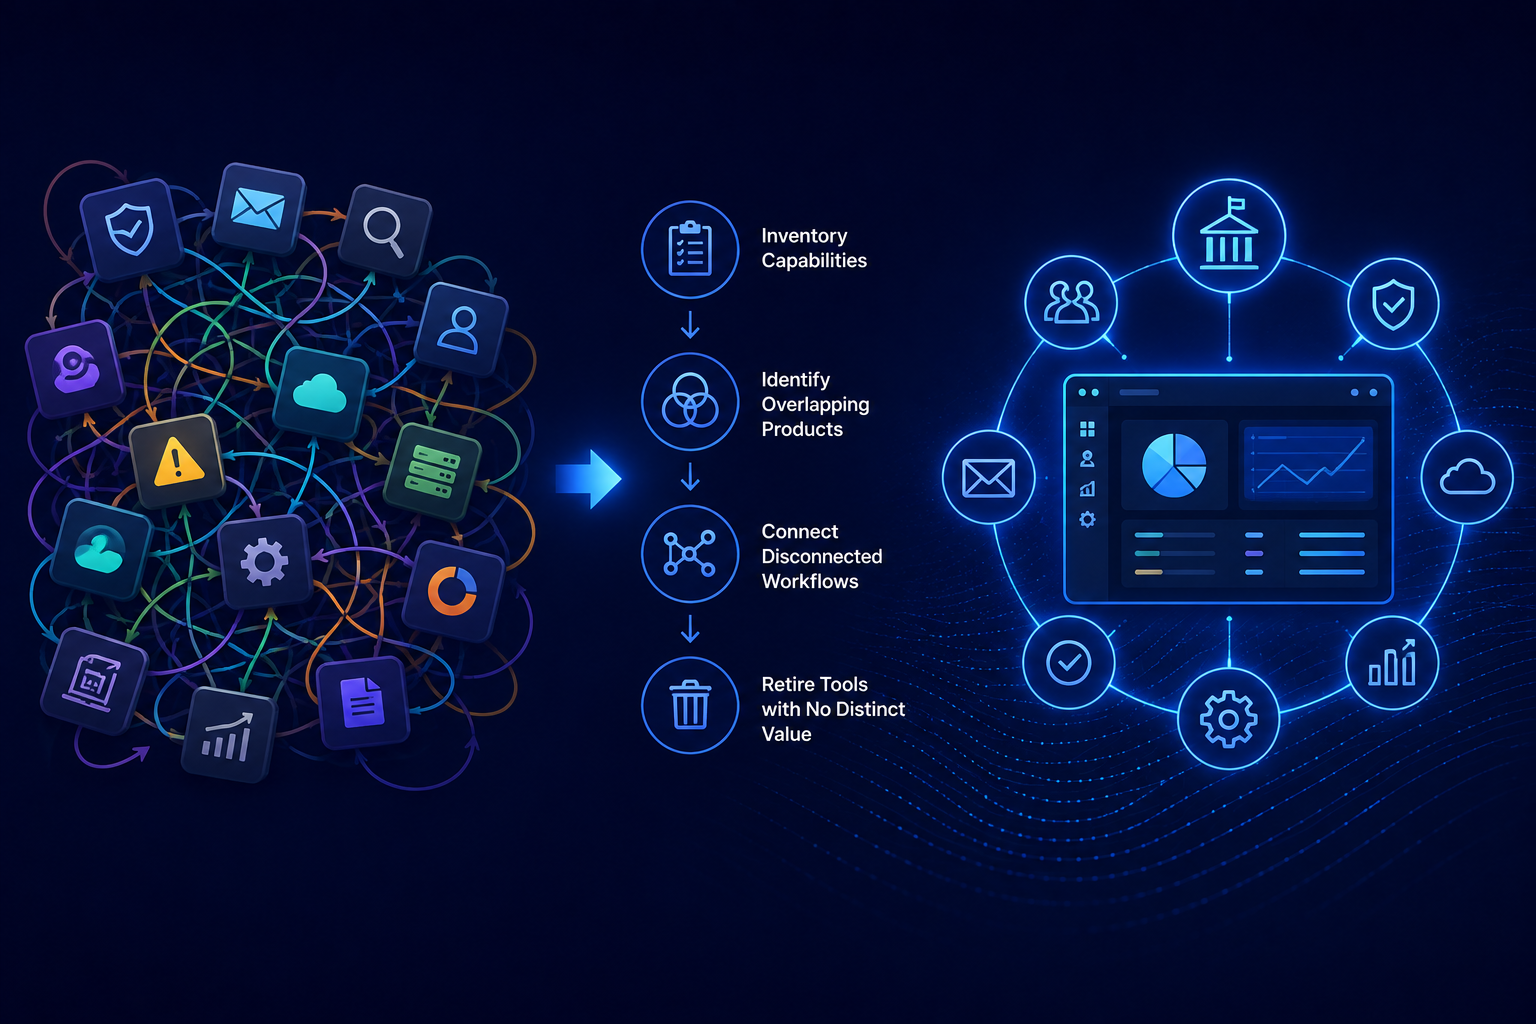
2. Consolidate Tools: Reduce tool fragmentation by adopting unified platforms that integrate detection, investigation, and response workflows.
3. Focus on Attack Chain Detection: Prioritize solutions offering broad visibility across endpoints, networks, cloud, and users to detect multi-stage attacks.
4. Invest in SOC Process Automation: Implement SOAR and automated case management to accelerate investigation and response times.
5. Measure Key Metrics: Track MTTD and MTTR alongside alert volume and analyst utilization to quantify SOC efficiency gains.
Where AgileBlue Fits
AgileBlue exemplifies AI-native SecOps principles by combining an autonomous AI-driven detection and response platform with 24/7 human analyst oversight. Its architecture was designed from the ground up to automate large portions of analyst work while providing full attack chain visibility and consolidating multiple security operations under one platform. This integration reduces tool sprawl and streamlines security operations workflows, helping organizations improve threat response times without growing their analyst teams.
Schedule Your Free Consultation to Explore Autonomous Response Security
Understanding how AgileBlue compares to Huntress’s Agentic Security Platform is the first step to reducing analyst burnout and improving your security posture. Contact us to discuss your unique environment, explore product capabilities, and see how a unified AI-driven security solution could transform your SOC’s effectiveness while controlling operational costs.
FAQ
Q: What is an autonomous response in cybersecurity?
A: Autonomous response refers to security technologies that automatically execute investigation and containment actions when a threat is detected, without waiting for manual approval. This accelerates mitigation and reduces the workload on security analysts.
Q: How does attack chain detection improve SOC efficiency?
A: By correlating events across all stages of a cyberattack, attack chain detection provides a comprehensive view that prioritizes true threats. This helps analysts focus on critical incidents and avoid chasing false positives.
Q: Does AgileBlue replace the need for multiple standalone security tools?
A: AgileBlue can consolidate selected capabilities. AgileBlue integrates capabilities found in SIEM, SOAR, EDR/XDR, and vulnerability management tools into one cohesive system, reducing the complexity and costs associated with managing multiple disjointed products.
Q: Is adopting autonomous response security suitable for all organizations?
A: While autonomous response enhances SOC efficiency for many organizations, adoption depends on security maturity, risk tolerance, and compliance requirements. Evaluating platform capabilities and alignment with organizational policies is essential.
Q: How does AgileBlue compare to Huntress for organizations that want to simplify security operations without hiring more analysts?
A: AgileBlue reduces manual workload and streamlines attack detection across the security stack by automating routine alert triage and providing full attack chain visibility, with humans reviewing escalations rather than every alert. Huntress takes the opposite structure: its Agentic Security Platform accelerates investigation, but a human analyst still makes every final call. Which fits better depends on whether your team wants automation as the front line or AI-assisted support for a fully human-led decision process.