Municipal ransomware protection is a layered program of defense and response tactics. The defense side hardens systems and identities to stop most intrusions. The response side rehearses detection, containment, and recovery so that attacks that get through are contained rather than shutting down public services. The whole program is built for the realities of local government: lean IT teams, legacy systems, and CJIS-regulated data.
Why Are Municipalities a Frequent Ransomware Target?
Critical services like 911 dispatch, water, courts, and elections often share the same under-resourced networks, so one intrusion can halt services residents depend on. Most local-government teams are small. KnowBe4 found the majority of SLTT organizations run with fewer than five dedicated security staff. The stakes are real. In July 2025, St. Paul, Minnesota declared a state of emergency after ransomware forced the city to shut down much of its network, disrupting internal systems and online services. Although police, fire, 911, and emergency operations remained available, the incident required an extended recovery effort that lasted weeks.
Part 1: Ransomware Defense Tactics For Municipal Governments
Most municipal ransomware succeeds through a few predictable openings. Closing them is the highest-return work a lean team can do. These ransomware defense tactics map to the NIST Cybersecurity Framework 2.0 and CISA’s StopRansomware guidance.
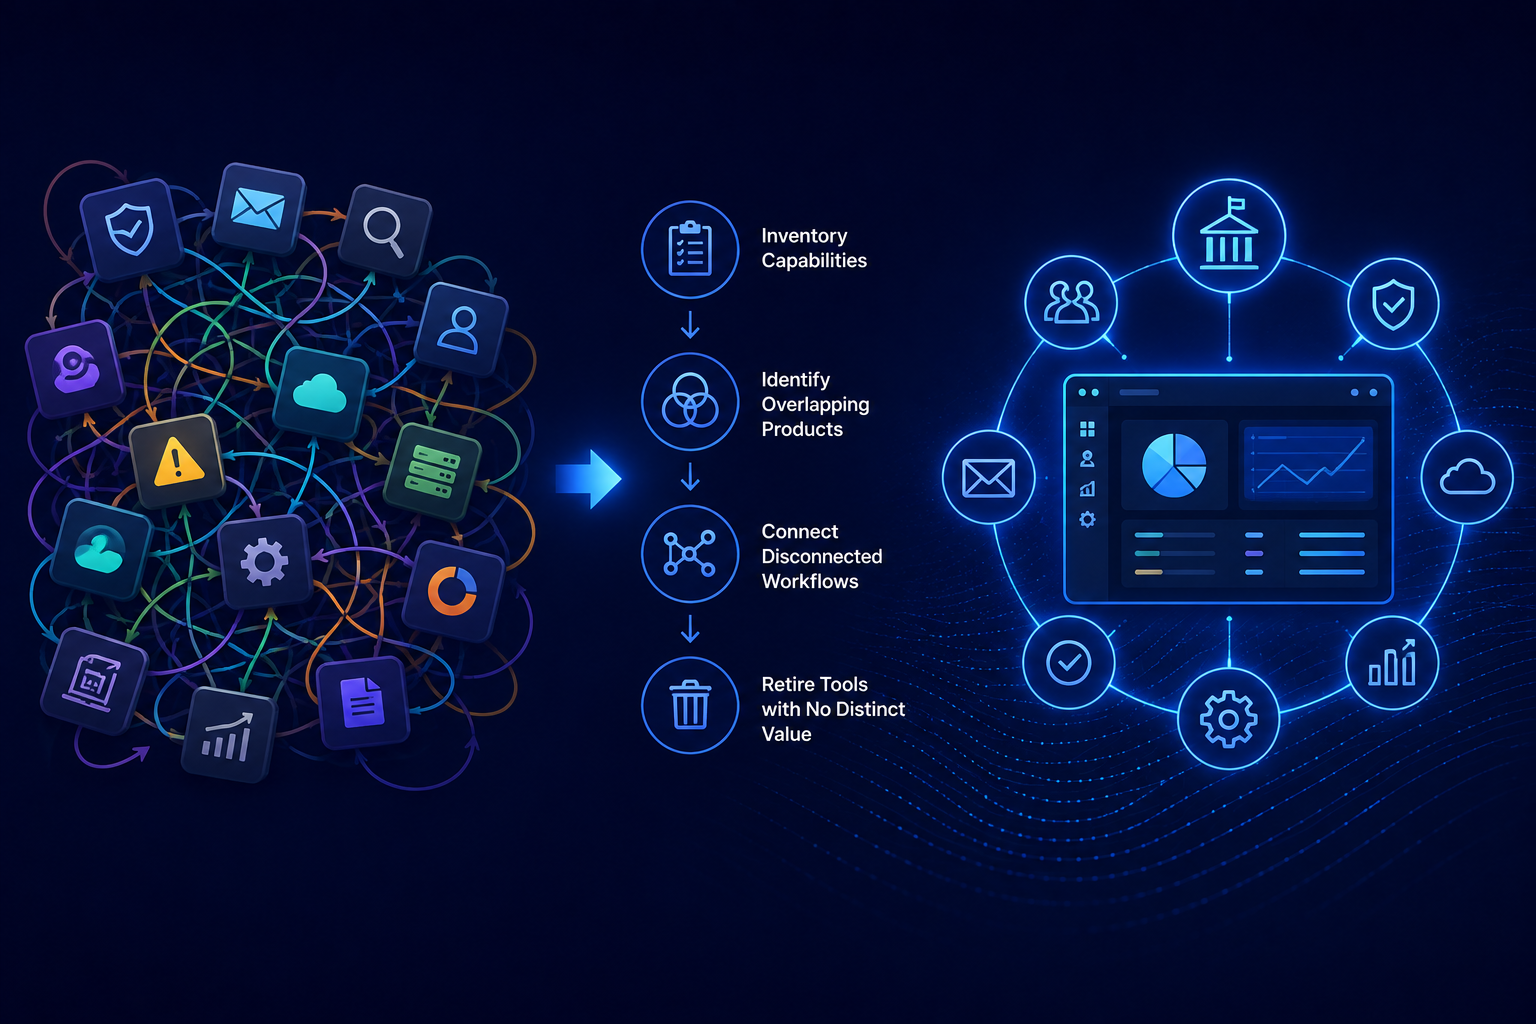
1. Inventory and prioritize.
Map your mission-critical systems, including water, dispatch, courts, elections, and finance, and rank them by service impact so you know what to protect and restore first. Effective ransomware protection also requires visibility across the entire environment, including endpoints, servers, networks, user identities, email platforms, cloud environments, SaaS applications, and exposed vulnerabilities. Connecting these data sources helps security teams recognize related activity that may appear harmless when alerts are viewed individually.
2. Close the common entry points.
Patch internet-facing systems promptly, tightly control or disable RDP, and require phishing-resistant multifactor authentication (MFA) for remote and privileged access. Isolate legacy systems that cannot be patched and continuously monitor user identities for suspicious sign-ins, privilege escalation, impossible travel, or unusual account activity. Many ransomware attacks begin with compromised credentials long before malware is deployed.
3. Segment and enforce least privilege.
Keep operational systems, administrative networks, backups, and other critical services separated so an intrusion cannot spread across the environment. Limit every user and administrator to only the access required for their role. Strong segmentation helps contain ransomware before attackers can move laterally or reach critical municipal services.
4. Protect and test backups.
Keep offline or immutable backups isolated from production systems. Following CISA guidance, regularly test that critical services can be restored—not simply that backup files exist. Recovery testing should verify data integrity and confirm that systems can be restored in the correct sequence to minimize disruption to municipal operations.
5. Defend the inbox and train.
Phishing remains one of the most common ransomware entry points. Combine advanced email filtering with recurring phishing awareness training that helps employees recognize evolving social engineering techniques. Reducing successful phishing attempts significantly lowers ransomware risk.
6. Choose a monitoring and response model.
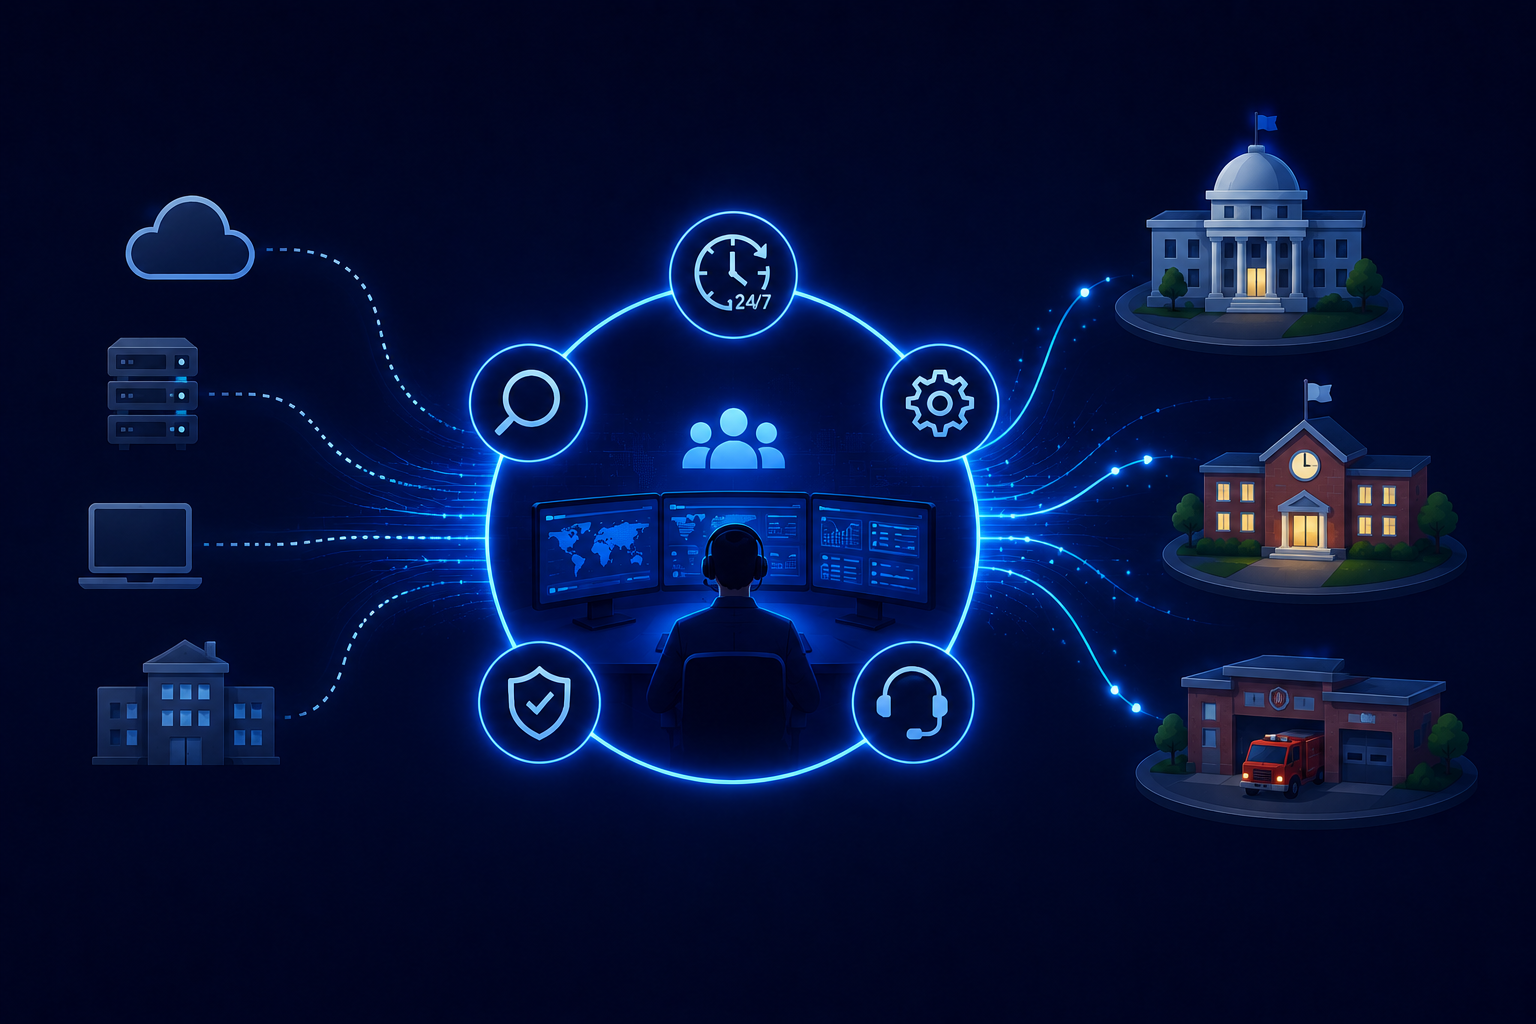
Detection only helps if someone can investigate and respond around the clock, which is difficult for many municipal IT teams. An effective security program should correlate activity across endpoints, identities, email, cloud environments, networks, and vulnerabilities to determine whether suspicious events are isolated or part of a larger attack. Automating routine investigation steps helps reduce false positives and allows analysts to focus on genuine threats.
Options range from managing EDR and SIEM internally to partnering with a managed SOC or adopting an AI-native SecOps platform with 24/7 SOC support. Select the approach that provides continuous visibility, rapid investigation, and timely response within your staffing and budget constraints.
Part 2: Ransomware Response And Recovery When Prevention Fails
Assume prevention will sometimes fail. For a lean team, the difference between a contained incident and a multi-week crisis is a response plan written and rehearsed before the attack.
Build the plan before you need it. Pre-decide the hard calls: who can disconnect systems, who speaks to residents and council, and which legal, law-enforcement, and CISA/MS-ISAC contacts to reach. Assign roles by name and rehearse regularly.
What to do in the first hour
1. Isolate affected systems to stop the spread, but do not wipe evidence.
2. Activate the plan and stand up the response team with its assigned roles.
3. Notify CISA, the FBI, and MS-ISAC early for government-specific support.
4. Don’t pay reflexively. CISA discourages payment. Decide with legal counsel and law enforcement, not under first-hour pressure.
Recover in the right order. Restore critical services first, in sequence, from clean, verified backups. Confirm systems are free of persistence before reconnecting so a reinfection can’t cascade back.
Communicate and close the loop. Use pre-drafted holding statements for residents, council, and regulators. Afterward, run a root-cause review, close the entry vector, and update the plan.
Frameworks And Compliance For Public Sector Cybersecurity
Anchor to public-sector standards, not healthcare rules. Use the CJIS Security Policy for law-enforcement data, the NIST Cybersecurity Framework 2.0 as the organizing model, and CISA’s #StopRansomware guidance for government-specific controls. Add CISA’s election and water-sector guidance where those systems apply.
How To Fund Municipal Ransomware Protection
Municipalities can fund ransomware protection through a combination of local budgets, state-administered grants, shared cybersecurity services, and public-sector programs. The State and Local Cybersecurity Grant Program (SLCGP) provided four years of funding through FY2025 and required states to pass at least 80% of their allocations to local governments. Because funding was distributed through states and territories rather than directly by CISA, municipalities should contact their state administrative agency or cybersecurity planning committee to determine whether previously awarded funding, statewide services, or related state programs remain available.
MS-ISAC also provides state, local, tribal, and territorial governments with threat intelligence, 24/7 SOC access, incident response support, and other cybersecurity resources. MS-ISAC now operates under a fee-based membership model, although certain CIS resources remain available at no cost and qualifying smaller organizations may be eligible for hardship assistance. Municipalities should evaluate current eligibility, costs, and available services as part of their cybersecurity planning and budgeting process.
Where AgileBlue Fits
For public-sector teams that can’t staff detection and response around the clock, AgileBlue supplies the always-on layer this playbook calls for. AgileBlue is an autonomous, AI-Native SecOps platform. Its agentic AI, Sapphire AI, detects, investigates, and makes real-time response decisions across endpoints, identity, and cloud. U.S.-based SOC analysts back it up and validate the high-stakes calls.
It’s the model behind our approach: AI when you need speed, humans when you need certainty. For a lean municipal team, that means proactive, 24/7 coverage and a security partner that acts on threats rather than just flagging them, without the cost of building an internal SOC.
Talk Through Your Municipality’s Ransomware Readiness
Every municipality starts from a different place. We’ll review your defenses, response plan, and funding options, then help you build a proactive, layered program that fits your team and budget. Request a consultation to start.
Frequently Asked Questions
Q: What is the best way to protect a municipal government from ransomware?
A: Layer defense and response. Harden systems with patching, phishing-resistant MFA, segmentation, and tested offline backups. Then run a rehearsed incident-response plan and 24/7 monitoring, whether in-house, through a managed SOC, or with an AI-Native SecOps platform sized to a lean team.
Q: What are the most important ransomware defense tactics for a city?
A: Patch internet-facing systems, require phishing-resistant MFA, segment the network, keep tested offline backups, and train staff against phishing. These close the entry points behind most municipal ransomware.
Q: What should a city do in the first hour of a ransomware attack?
A: Isolate affected systems without destroying evidence, activate the incident-response plan, and notify CISA, the FBI, and MS-ISAC. Don’t pay reflexively. CISA discourages payment, so involve legal counsel and law enforcement in the decision.
Q: What compliance frameworks apply to public sector cybersecurity and ransomware defense?
A: The CJIS Security Policy governs law-enforcement data, the NIST Cybersecurity Framework 2.0 is the organizing model, and CISA’s #StopRansomware guidance adds government-specific controls. Elections and water systems have their own CISA guidance.