AgileBlue is a strong SilverSky alternative for lean security teams that need AI-native SecOps, proactive risk visibility, and accessible human support in one platform. The best choice depends on whether your team needs unified detection and response, standalone security tools, or a managed service that reduces operational workload.
Choosing an alternative is not simply a feature-matching exercise. Lean teams must evaluate how much investigative, integration, and remediation work a provider leaves with internal staff. AgileBlue’s AI-native SecOps platform combines automation with a U.S.-based team of cyber experts, giving organizations broad coverage without requiring them to build a full security operations center.
SilverSky Alternatives for Lean Security Teams
The best SilverSky alternatives combine broad visibility, automated response, vulnerability management, and practical human guidance. AgileBlue fits organizations that want these capabilities connected through an AI-native environment rather than spread across separate tools and providers.
The main alternatives generally fall into four categories:
| Alternative Model | Best Fit | Main Advantage | Potential Tradeoff for Lean Teams |
|---|---|---|---|
| AI-native SecOps platform | Teams seeking unified operations | Integrated automation, risk visibility, and human support | Buyers must validate integrations, onboarding, and response authority |
| Large enterprise security platforms | Mature teams with specialized analysts | Extensive capabilities and technology ecosystems | Licensing, tuning, and administration may require greater internal capacity |
| Managed security or MDR provider | Teams seeking to outsource security operations | Continuous monitoring, investigation, and analyst support | Coverage and remediation responsibilities vary by contract |
| Multiple point solutions | Teams with specialized technical requirements | Freedom to select a product for each control | Integrations, alert triage, renewals, and vendor management remain internal |
Before selecting a provider, document which responsibilities your team wants to retain. Ask every vendor who tunes detections, investigates alerts, coordinates response, manages vulnerabilities, and reports risk to leadership. A broad feature list has limited value if two internal employees must connect and operate every component.
SilverSky vs. AgileBlue for AI-Native SecOps
SilverSky uses an environment-first managed security model that operates across customer-owned and partner technologies, including Torq’s AI SOC Platform. AgileBlue delivers security operations through its own unified platform, with Sapphire AI embedded across detection, investigation, and customer-authorized response. Lean teams should compare the resulting workflows, response authority, implementation requirements, and measurable outcomes rather than assuming that native or partnered technology is inherently better.
SilverSky offers managed XDR, managed EDR, vulnerability management, network protection, email protection, Microsoft 365 and Azure services, security awareness training, and consulting. That breadth may suit organizations seeking multiple managed cybersecurity services.
A useful evaluation should include a live workflow rather than a slide presentation. Give each provider the same scenario, such as a compromised identity followed by suspicious cloud activity, and ask them to demonstrate:
- How the platform correlates the events
- Which actions occur automatically
- When a human analyst intervenes
- What evidence and context the customer receives
- Which remediation tasks remain with the internal team
This exercise exposes operational differences that feature checklists often hide.
How Can a SilverSky Alternative Reduce Alert Fatigue?
A SilverSky alternative can reduce alert fatigue by correlating related signals, prioritizing them by risk, and automating repeatable investigative or response tasks. AgileBlue applies advanced algorithms to essential security data, so lean teams can focus on consequential decisions instead of treating every alert as an isolated event.
Alert reduction alone is not the right goal. A system that suppresses too much activity may hide important signals. Teams should instead measure whether the provider turns raw detections into contextual, actionable incidents.
Ask prospective providers to report these four measures during a pilot:
1. The number of raw signals ingested
2. The number of incidents presented to your team
3. The percentage of incidents investigated or contained without internal action
4. The median time from detection to a documented response decision
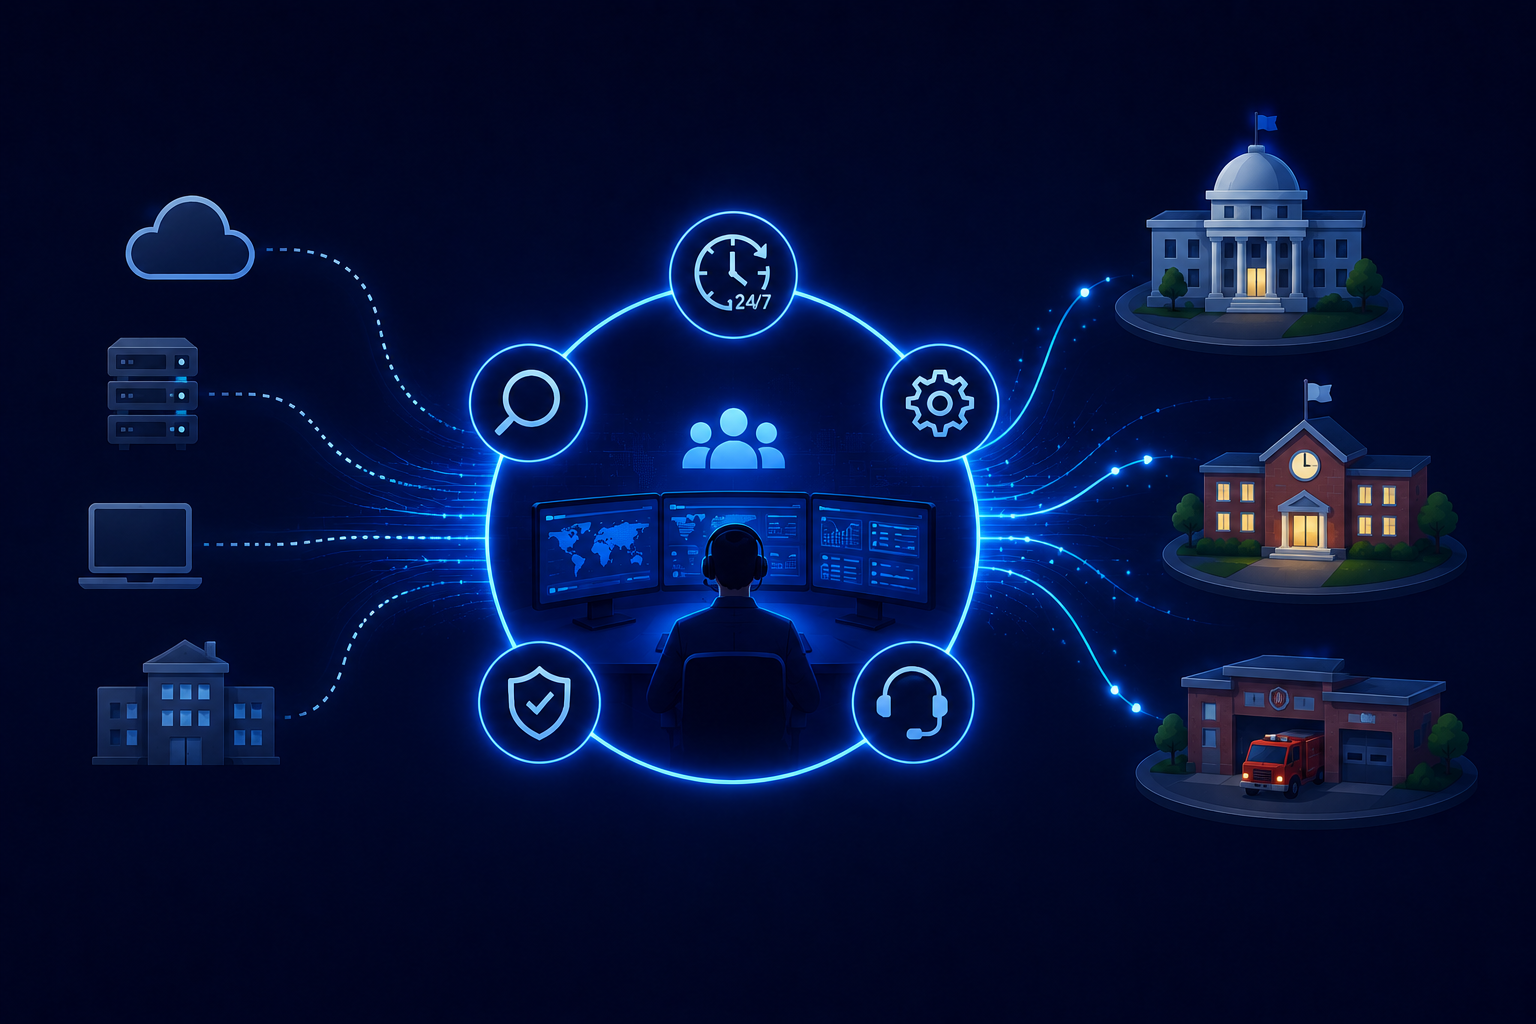
AgileBlue’s AI-native SecOps Platform is designed to orchestrate and autonomously respond across endpoints, networks, and cloud systems through native integrations. The platform also analyzes user behavior and applies machine learning to identify activity that matters to each client’s environment.
Which Capabilities Matter Most to a Lean Security Team?
The most important capabilities are unified visibility, automated investigation and response, continuous vulnerability discovery, and direct access to knowledgeable security professionals. AgileBlue combines these functions so a small internal team can manage risk without stitching together separate operational workflows.
Prioritize the following capabilities during your evaluation:
- Native automation: Confirm whether orchestration is part of the core platform or an add-on requiring separate configuration.
- Cross-environment monitoring: Look for coverage across endpoints, networks, cloud services, applications, Kubernetes, and APIs where relevant.
- Continuous vulnerability scanning: Select scanning that discovers assets dynamically and identifies new vulnerabilities without waiting for a periodic assessment.
- Risk-based prioritization: Require a ranked action plan that connects vulnerabilities and alerts to business impact.
- Human response support: Establish who is available during an incident, how quickly they engage, and what remediation assistance is included.
- Executive reporting: Request reports that translate technical findings into risk, progress, and compliance evidence.
- Strategic guidance: Confirm that security maturity assessments, tabletop exercises, and roadmap planning are available when the program needs them.
Our vulnerability scanning can run through device-level agents or a network sensor. It provides continuous scanning, new-device alerts, dynamic asset discovery, and segmented network views while maintaining low network utilization.
Do not accept “24/7 monitoring” as a complete answer. Request the escalation matrix, response boundaries, communication channels, and three anonymized incident examples before signing a contract.
SilverSky vs. AgileBlue Support for Small Security Teams
Our support model combines platform automation with consistent access to real people. The available SilverSky comparison materials identify communication and tool usability as potential evaluation points, but lean teams should verify current service terms and test both providers directly. Support experiences can differ by package and account.
Technology does not eliminate the need for clear communication during a security incident. Our team breaks down technical information during a crisis and provides regular update meetings, one-on-one support, and access to security professionals between incidents.
Support evaluation should go beyond promised response times. During procurement, submit a sample ticket, request a technical explanation, and ask who owns the issue when multiple technologies are involved. A lean team needs continuity, not repeated handoffs that require staff to restate the same context.
AI-Native SecOps vs. Traditional Managed Security
AI-native SecOps is the better fit when a lean team wants automation and unified decision support. Traditional managed security may suit organizations that primarily want outsourced monitoring for a defined technology stack. Our model combines AI-powered correlation and autonomous response with analyst and advisory support.
The operational differences include:
- AI-native SecOps: Correlates data across security layers, prioritizes risk, and automates selected response actions.
- Traditional managed security: Monitors agreed systems and escalates detections according to the service scope.
- Point-tool strategy: Gives the buyer control over individual products but leaves integration and workflow ownership with the internal team.
No model is universally best. A company with a mature security engineering function may prefer specialized products and extensive customization. A lean team usually gains more value from fewer interfaces, shared context, and a provider that can carry investigations through to a documented response.
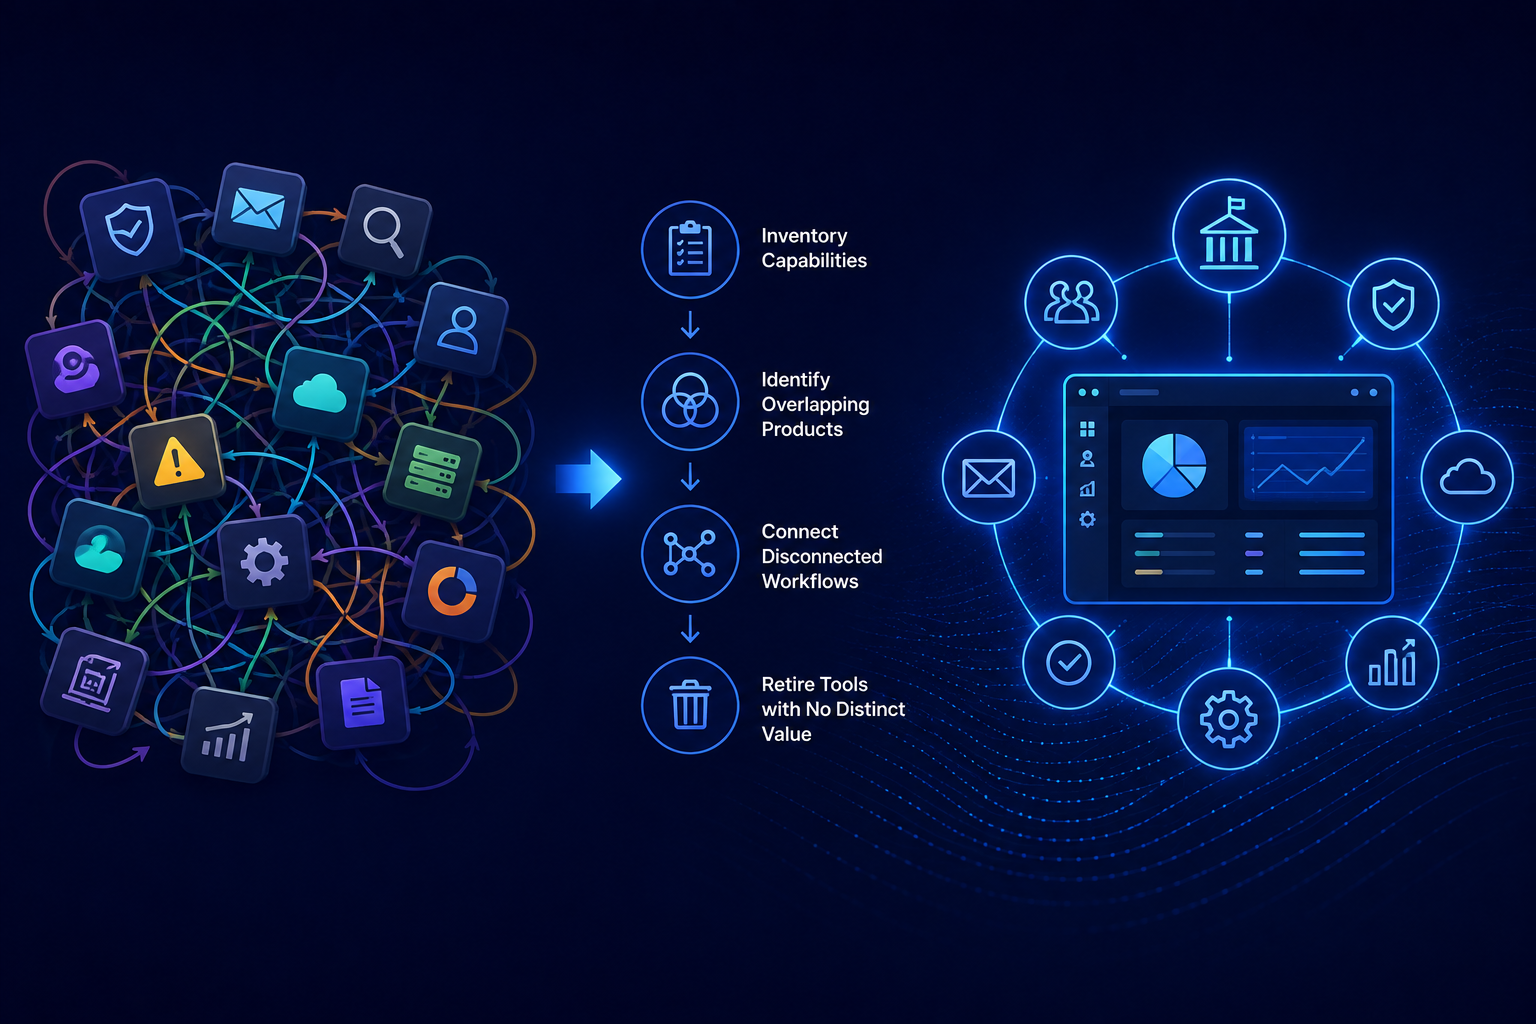
We recommend mapping every existing tool, annual contract, integration, and owner before comparing costs. Include internal labor, after-hours coverage, implementation, and vendor management. A lower subscription price can become more expensive when staff must tune several products and reconcile disconnected reports.
Why AgileBlue Is a Strong SilverSky Alternative
AgileBlue is a strong SilverSky alternative because we connect AI-powered automation, broad security visibility, proactive risk management, and human expertise in one operating model. This approach is built for organizations that need capable security operations without adding a large internal SOC.
Three parts of our model stand out:
- Sapphire AI autonomously detects, investigates, and responds to attacks across endpoint, network, and cloud environments.
- Our cloud-based technology uses machine learning and user behavior analytics, backed by a U.S.-based team of cyber experts.
- The Strategic Advisory Group provides security maturity assessments, tabletop exercises, ongoing guidance, and actionable security roadmaps.
These capabilities have supported organizations in regulated industries. PerfectServe developed a 12-month Security Operations Roadmap covering risk assessments, a cybersecurity committee, and its first tabletop exercise.
The right provider should improve security operations and make risk easier to communicate. Our model pairs autonomous technology with practical guidance, so lean teams receive both operational capacity and a path toward greater cyber resilience.
Compare Your Security Operations Options
We can review your current tools, alert workload, vulnerability management process, and response responsibilities to identify where an AI-native SecOps model could reduce complexity. Request a demo to see how our platform correlates activity, prioritizes risk, and supports response across your environment.
Bring a real workflow or recent incident scenario so our team can demonstrate how the operating model applies to your needs.
Frequently Asked Questions
Q: Can a small IT team use AI-native SecOps without a dedicated SOC?
A: Yes. A small IT team can use AI-native SecOps when the provider handles continuous monitoring, correlation, investigation, and selected response actions. Confirm which tasks are fully managed, which require approval, and which remain with your employees before choosing a service.
Q: How long does it take to switch managed security providers?
A: The timeline depends on data sources, endpoint count, cloud environments, integrations, and contract overlap. Build a transition plan that covers log ingestion, agent deployment, detection tuning, escalation testing, historical data, and the retirement of old tools. Keep both services active until critical monitoring and response workflows pass testing.
Q: Will replacing several security tools lower my total cost?
A: Consolidation can lower total cost when it reduces licensing, integration work, analyst time, and vendor management. Compare three-year costs rather than subscription fees alone. Include implementation, after-hours staffing, professional services, data ingestion, retention, and internal administration in the calculation.
Q: What proof should I request during a cybersecurity platform demo?
A: Ask the provider to investigate a realistic incident from detection through response. The demo should show event correlation, risk priority, analyst context, automated actions, customer approvals, remediation guidance, and executive reporting. Avoid relying on prerecorded interface tours that do not reflect your environment.
Q: How should buyers compare SilverSky;s partnered AI with AgileBlue’s Native AI?
A: Buyers should compare operational outcomes rather than technology ownership alone. Ask which investigations and response actions are automated, which require human or customer approval, how the automation is governed and audited, and how detection and response performance is measured.