For companies with small security teams, choosing the best Managed Detection and Response (MDR) provider means balancing enterprise-grade protection with operational simplicity. AI-native SecOps platforms, like AgileBlue, have emerged as key players by reducing alert fatigue and automating response without adding headcount.
How Can Small Security Teams Reduce Alert Fatigue?
Small security teams often face overwhelming volumes of alerts, many false positives, and limited bandwidth to triage incidents effectively. Reducing alert fatigue starts with adopting MDR solutions that prioritize meaningful threats over alert volume. Key strategies include:
- AI-Based Alert Triage: Leveraging AI models trained to identify attack patterns rather than isolated alerts helps reduce noise. This approach shifts focus from raw alert volumes to validated attack incidents.
- Automated Case Management: Automating benign case closures and using orchestration workflows saves valuable analyst time and effort.
- Focused SOC Staffing: A lean team supported by MDR partners gains 24/7 support to cover off-hours and incident response, relieving burnout and operational gaps.
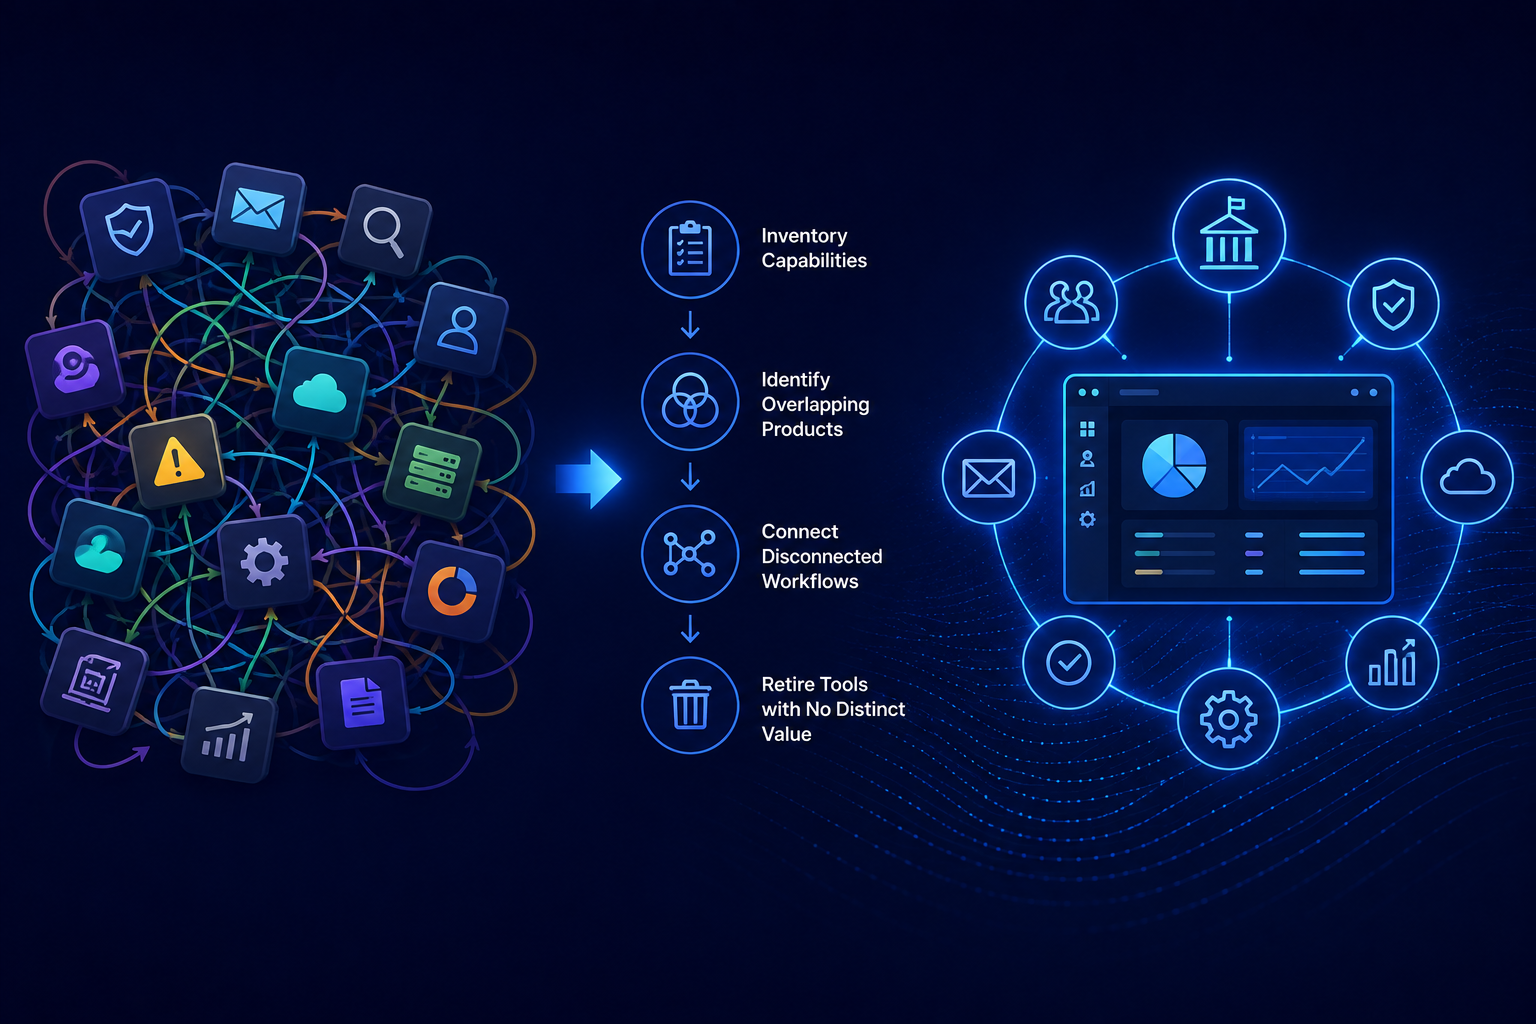
- Integration and Consolidation: Combining endpoint, network, and cloud monitoring in one platform eliminates silos that cause fragmented alerting and duplicated work.
Effective fatigue reduction demands MDR providers capable of tailored alert tuning and operational collaboration with in-house teams.
Comparing SilverSky MDR and AgileBlue for Lean Teams
When evaluating MDR providers for smaller security operations, two models dominate the conversation: traditional MDR from providers and AI-native SecOps approaches like AgileBlue.
SilverSky MDR Overview
SilverSky offers a comprehensive MDR service emphasizing human-led threat hunting, involving dedicated analysts who investigate alerts from a variety of integrated sources. In May 2026, SilverSky announced a strategic partnership with Torq, layering the Torq AI SOC Platform, which combines agentic AI, contextual reasoning, and autonomous execution, onto its existing human-led model to accelerate triage, investigation, and response. This is a partnered capability rather than an in-house-built platform, which is worth noting when comparing it to providers that built agentic AI into their own architecture from the start.
Questions lean security teams should ask:
Because SilverSky’s Torq partnership is relatively new and service capabilities may differ by package, prospective customers should confirm how AI and automation operate within their specific MxDR engagement. Key questions include:
- How deeply is Torq integrated into the service? Ask which SilverSky MxDR packages include Torq and whether it supports the full investigation and response workflow or selected activities.
- Which activities are fully automated? Determine which triage, enrichment, investigation, containment, and remediation tasks can be completed automatically and which require a SilverSky analyst.
- What requires customer approval? Confirm which response actions SilverSky can perform immediately, which must be authorized in advance, and which remain the customer’s responsibility.
- How is alert reduction measured? Ask how SilverSky defines false positives, confirmed incidents, and customer escalations, and what percentage of activity ultimately reaches the internal team.
- What implementation work is required? Review which technologies and telemetry sources are supported, what integrations must be configured, and whether existing tools can remain in place.
- How is performance reported? Ask whether customers receive defined metrics for detection, investigation, containment, and response times, along with visibility into how those results are calculated.
AgileBlue Overview
AgileBlue’s AI-native SecOps platform embeds AI throughout detection, investigation, and autonomous response, analyzing attacks as sequences rather than isolated alerts. This enables accelerated and proactive threat containment.
Strengths:
- Sapphire AI automates repeatable Tier 1 and 2 investigation work and closes cases determined to be benign.
- The platform correlates related activity across the environment to identify broader attack patterns rather than evaluating every signal in association.
- Customer-defined response preferences determine which actions Sapphire AI can execute autonomously and when SOC analyst involvement is required.
- AgileBlue combines security data, detection, investigation, response, endpoint visibility, cloud security, vulnerability management, and threat exposure management within one operating environment.
- AgileBlue reports an average Mean Time to Detect of 4.6 minutes and gives customers visibility into MTTD, autonomous MTTR, and analyst MTTR.
Considerations:
- The technology-centric approach requires buy-in from security teams accustomed to manual processes.
- Human analyst oversight remains critical for governance and complex cases.
- Selection of platform should consider industry and regulatory needs.
SilverSky MDR Overview
SilverSky delivers 24/7 managed detection and response through an expert-led security operations model. Its MxDR services include continuous monitoring, investigation of suspicious activity, customer-specific escalation procedures, coordinated response, reporting, and ongoing detection tuning.
In May 2026, SilverSky announced a strategic partnership with Torq to incorporate the Torq AI SOC Platform into its security operations strategy. SilverSky says the partnership adds AI-driven investigation, response orchestration, and autonomous execution while preserving human judgment, transparency, and operational accountability.
SilverSky offers multiple MxDR options, including services designed around broader consolidated coverage and Microsoft security environments. The specific technologies, integrations, automation capabilities, and response services available may therefore depend on the selected package and contract.
Questions Buyers Should Ask:
- Which investigation and response activities are automated through Torq?
- Which actions require a SilverSky analyst or customer approval?
- Is the Torq capability included in every MxDR package?
- Which containment and remediation actions are included in the contracted service?
- How are detection, investigation, and response times calculated and reported?
- What integrations and implementation work are required for the customer’s environment?
Practical Recommendations for Small Security Teams Choosing MDR
- Evaluate Automation Depth: Choose MDR providers whose AI capabilities actively reduce alert volume versus those delivering raw alerts for manual triage.
- Assess Integration Breadth: Look for solutions integrating seamlessly with your endpoints, network, cloud, and existing tools to avoid data gaps.
- Demand Transparent Alert Context: Effective MDR should provide rich context and actionable insights, not just alerts.
- Factor Support Models: Consider 24/7 SOC availability and advisory services tailored to lean teams.
- Prioritize Scalability: Expect your MDR to scale as your security maturity grows, without requiring proportional increases in in-house staff.
- Ask Whether Agentic AI Is Native or Partnered: Some providers, including SilverSky (via its Torq partnership), added agentic AI through a third-party platform rather than building it into their own architecture. Ask how deeply that integration goes, full workflow automation, or a bolt-on for select tasks, since the answer affects how much manual triage genuinely goes away.
Why AgileBlue Represents a New Approach in MDR for Small Security Teams
AgileBlue’s AI-native SecOps platform exemplifies how combining agentic AI with human SOC expertise can reduce alert fatigue without expanding headcount. Designed for mid-market organizations with lean IT teams, it integrates multiple security modules into a unified platform. Its autonomous response capabilities automate large portions of analyst workflows, focus on the attack chain rather than alerts, and drive rapid detection times that shrink risk windows.
This innovative model supports small teams by eliminating silos and noise, freeing analysts to focus on critical threats, and delivering enterprise-grade protection tailored to mid-sized organizations.
Get Started With the Best MDR Approach for Your Team
Choosing between SilverSky and AgileBlue depends on your team’s size and appetite for automation. Lean security operations should prioritize solutions offering deep automation, unified visibility, and strong collaboration from SOC experts.
FAQ
Q: What are the main differences between SilverSky and AgileBlue?
A: SilverSky and AgileBlue both combine AI, automation, and human security expertise. SilverSky delivers an expert-led MxDR service and is integrating Torq’s AI SOC Platform to accelerate investigation, orchestration, and response. AgileBlue delivers these capabilities through its AI-native SecOps platform, where Sapphire AI continuously investigates activity, closes benign cases, and initiates customer-authorized response actions with support from 24/7 SOC analysts. Buyers should compare how much work each model automates, which response actions are included, when human involvement is required, and how performance is measured.
Q: How does alert fatigue impact small security teams?
A: Alert fatigue leads to analyst burnout, missed true positives, and slower threat response. Small teams with limited staff face increased risk when overwhelmed by high volumes of low-value alerts.
Q: Can small security teams operate effectively without expanding headcount using MDR?
A: Yes. By adopting MDR providers with AI-driven automation and 24/7 SOC support, small teams can extend coverage and focus expertise where it matters most, avoiding adding full-time staff.
Q: What should small teams look for when evaluating an MDR provider?
A: Key factors include depth of automation, integration with existing security tools, transparency in alert context, 24/7 expert support, and scalability aligned with organizational growth.