How Does Cooperative Procurement Work for State and Local Government Cybersecurity Purchases?
Cooperative procurement allows state and local government agencies to streamline cybersecurity acquisitions by leveraging pre-negotiated contracts established through joint purchasing programs. This process simplifies compliance with public procurement rules and accelerates access to vetted cybersecurity solutions tailored for SLED (state, local, education) organizations.
What Is Cooperative Procurement in State and Local Government Cybersecurity Buying?
Cooperative procurement is a method where multiple public agencies combine their purchasing power to enter into a single contract with a vendor. This approach helps state and local governments acquire cybersecurity products and services more quickly and cost-effectively by using pre-negotiated terms, pricing, and contract language established by cooperative purchasing organizations or lead public agencies.
Cybersecurity procurement using cooperative agreements must comply with state and local procurement regulations but removes duplicative efforts across departments and jurisdictions. Instead of conducting repetitive, individual bids or requests for proposals (RFPs), agencies tap into cooperative contracts that often include cybersecurity vendors vetted for compliance, reliability, and best practices.
This method can cover a range of cybersecurity needs, including managed detection and response, incident response services, endpoint protection, risk assessments, and cloud security. Cooperative contracts may include public-sector terms, but agencies must verify whether the contract and proposed solution satisfy their specific security, privacy, data-handling and regulatory requirements. These requirements may include the CJIS Security Policy, HIPAA, PCI DSS, GovRAMP, or NIST-aligned controls, depending on the agency, data, and use case.
What Are the Best Cooperative Purchasing Programs for SLED Cybersecurity Solutions?
Several cooperative purchasing programs have established themselves as reliable sources for cybersecurity procurement by state and local agencies:
- National Association of State Procurement Officials (NASPO) ValuePoint: NASPO ValuePoint uses a Lead State Model in which one state conducts a competitive solicitation and establishes a master agreement that other participating states and eligible public entities may use. Access is not automatic: states typically adopt contracts through Participating Addenda that establish state-specific terms and identify which agencies, local governments, schools, and other entities are eligible. Before purchasing, an organization should confirm that its state participates in the specific agreement and that the desired cybersecurity products or services fall within the contract’s approved scope.
- OMNIA Partners Public Sector: OMNIA Partners provides access to cooperative contracts competitively solicited and awarded by lead public agencies, such as cities, counties, school districts, and public universities. Eligible state, local, and education organizations may use these master agreements to reduce duplicate solicitation work, but each organization remains responsible for confirming its eligibility, reviewing the contract’s scope and pricing, and following its own procurement laws, approval requirements, and internal policies.
- Sourcewell: Sourcewell is a Minnesota government entity that conducts competitive solicitations and awards cooperative contracts for use by eligible government, education, and nonprofit organizations. Membership is free, and participating organizations can purchase through awarded contracts without conducting a separate solicitation when permitted by their procurement rules. Each organization remains responsible for confirming that the contract is legally available to it, verifying that the proposed cybersecurity products or services fall within the awarded scope, and completing its own pricing, security, and compliance review.
- State-specific cooperative programs: Many states maintain cooperative contracts, statewide master agreements, or purchasing schedules that public agencies can use to acquire technology and cybersecurity services. Examples include Texas Department of Information Resources Cooperative Contracts and California’s Multiple Award Schedules and Leveraged Procurement Agreements. Eligibility, purchasing thresholds, approved products, authorized resellers, and ordering procedures vary by state and contract, so agencies should confirm that the agreement is available to them and that the proposed cybersecurity solution falls within its approved scope.
- GSA Cooperative Purchasing Program: Eligible state, local, and tribal government entities can use this program to purchase certain IT, cybersecurity, and law-enforcement products and services through the GSA Multiple Award Schedule. Only designated categories and participating vendors are available through the program, so agencies should verify their eligibility, confirm that the desired offering carries the appropriate Cooperative Purchasing designation, and follow their own procurement laws, approval processes, and security-review requirements.
Choosing the right cooperative program depends on the agency’s jurisdiction, specific security objectives, and contract details. Programs with broad adoption among peer agencies and clear regulatory compliance offer greater assurance in procurement.
How Can State and Local Governments Simplify Cybersecurity Procurement?
Several practical steps and recommended practices can make cybersecurity procurement more efficient through cooperative purchasing:
1. Clarify Local Procurement Guidelines: Agencies should verify procurement thresholds, required approvals, and the permissibility of cooperative contracts under local laws to prevent compliance issues.
2. Involve Key Stakeholders Early: Engaging IT security staff, procurement officers, legal counsel, and end users from the start fosters consensus on needs and vendor assessments.
3. Select Pre-Approved Vendors: Cooperative contracts list pre-qualified vendors, decreasing administrative overhead and accelerating solution deployment.
4. Standardize Evaluation Criteria: Using consistent frameworks tied to cybersecurity maturity models or standards like NIST CSF helps objectively assess vendor fit and capabilities.
5. Centralize Contract Management: Keeping organized records of contracts, vendor performance data, and security outcomes enhances sourcing efficiency and repeatability.
6. Evaluate Total Cost of Ownership: Agencies ought to consider ongoing support, integration effort, and training demands alongside upfront costs when making procurement decisions.
7. Utilize Available Resources and Expertise: Some states offer portals, advisory services, or peer-sharing forums that ease cooperative procurement navigation and decision-making.
Why Cooperative Procurement Matters for SLED Cybersecurity Investments
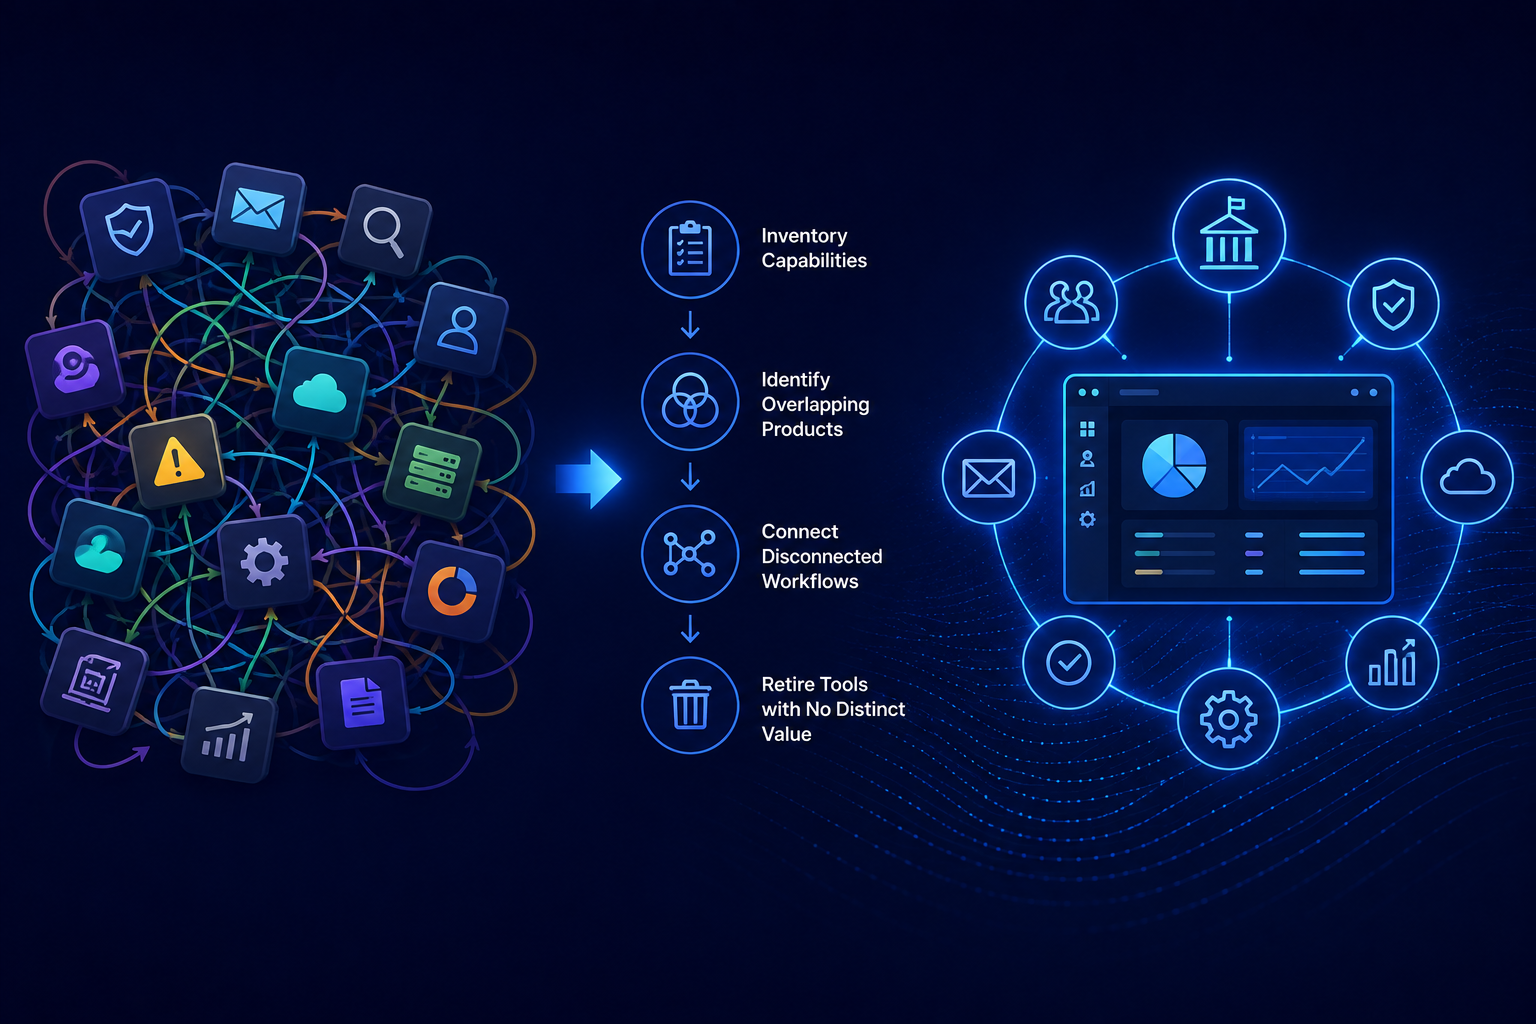
Cooperative procurement provides significant advantages for state and local governments managing cybersecurity investments with limited resources. Its benefits include faster procurement cycles, vendor consolidation, regulatory compliance management, and cost reductions through collective buying power.
With many SLED entities operating lean IT security teams, cooperative purchasing programs present a way to access mature cybersecurity solutions without engaging in lengthy, complex bidding processes. They also promote adherence to best practices by embedding vendor performance expectations and regulatory standards in contract terms.
How AgileBlue Supports Cooperative Procurement Cybersecurity Needs
The purchasing vehicle can simplify acquisition, but it should not replace a thorough evaluation of the cybersecurity solution itself. AgileBlue helps state, local, and education organizations strengthen 24/7 detection, investigation, and response through an AI-native SecOps platform supported by U.S.-based SOC analysts. The platform connects activity across endpoints, identities, email, networks, and cloud environments, helping lean public-sector teams reduce manual investigation and respond to threats according to their defined preferences.
During the procurement process, AgileBlue can provide the documentation agencies need to evaluate solution scope, integrations, implementation requirements, data handling, service responsibilities, pricing, and relevant security controls. Available purchasing options vary by jurisdiction and may include direct procurement, an authorized reseller or partner, or an applicable cooperative or statewide contract when available.
Before relying on a particular contract vehicle, agencies should confirm that they are eligible to use it, that AgileBlue or an authorized reseller is included, and that the proposed products and services fall within the contract’s awarded scope.
Next Steps in Leveraging Cooperative Procurement
Navigating cooperative procurement frameworks can be complex, but an informed approach unlocks significant efficiencies in acquiring cybersecurity technologies. Agencies are encouraged to deepen their understanding of available cooperative agreements applicable in their jurisdiction and align procurement strategies with operational needs.
FAQ
Q: What is the primary benefit of cooperative procurement for government cybersecurity purchases?
A: It offers state and local agencies access to pre-established contracts that reduce the time, expense, and complexity of procurement while maintaining regulatory compliance.
Q: Are all state and local government entities eligible to use cooperative purchasing programs?
A: Most can, but usage depends on specific local procurement rules. Some jurisdictions may have restrictions or additional approval processes, so agencies need to confirm applicability.
Q: Does cooperative procurement generally reduce costs for cybersecurity purchases?
A: Cooperative procurement may provide favorable pricing and reduce the administrative cost of conducting a separate solicitation, but it does not guarantee the lowest total cost. Agencies should validate the quoted price against the cooperative contract, compare available options, account for administrative fees and reseller markups, and evaluate implementation, support, renewal and exit costs.